Built for Hybrid Kubernetes GPU Infrastructure
The parts of a hybrid GPU cloud, from provisioning and tenant isolation to cross-region management and AI stacks.
Tenant Isolation
Tenant Clusters Across Your Infrastructure
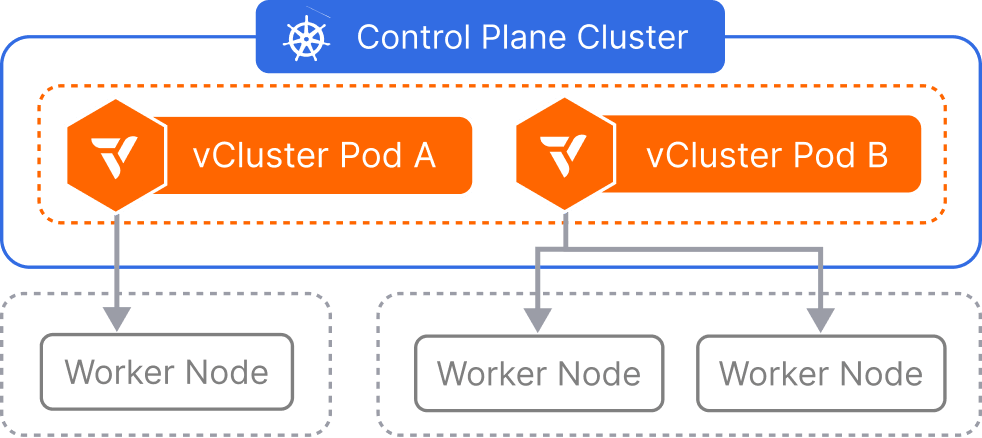
Each tenant has an independent Kubernetes API, data store and RBAC boundary. Lightweight control-plane hosting reduces dedicated server requirements for distributed GPU infrastructure; Private Nodes keep production workers tenant-specific.
Independent tenant API and data store
Tenant-scoped scheduling on Private Nodes
No dedicated control-plane servers per tenant
Hybrid Orchestration
Fleet Operations Across Infrastructure Locations
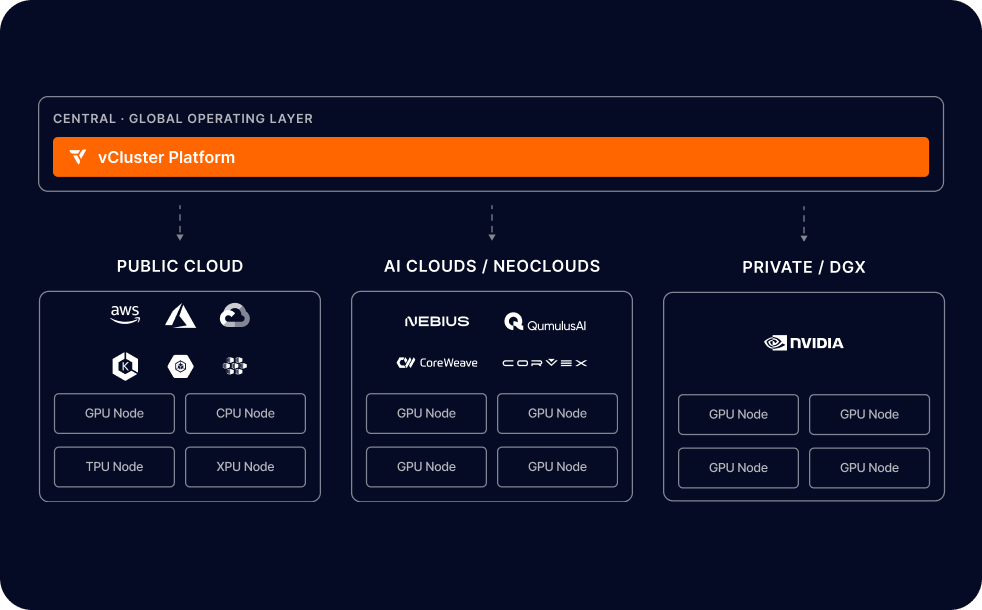
Manage distributed GPU infrastructure across supported clouds and data centers through one platform. Tenant control planes remain separate; plan worker placement, interconnects, data residency and failure domains for each location.
Bare Metal
Zero-Touch GPU Server Provisioning
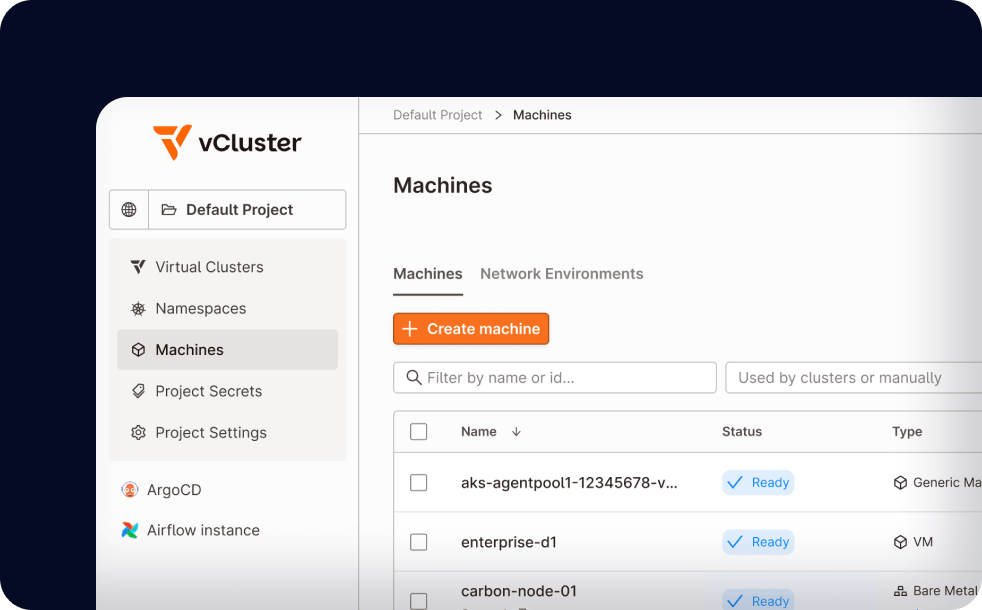
vMetal exposes one Machine API above bare metal and VM provisioning drivers. Registered inventory, images and credentials enable repeatable machine lifecycle workflows for distributed GPU infrastructure. Network automation uses supported integrations such as Netris.
Workload Security
Kernel-Native Isolation Without VM Overhead
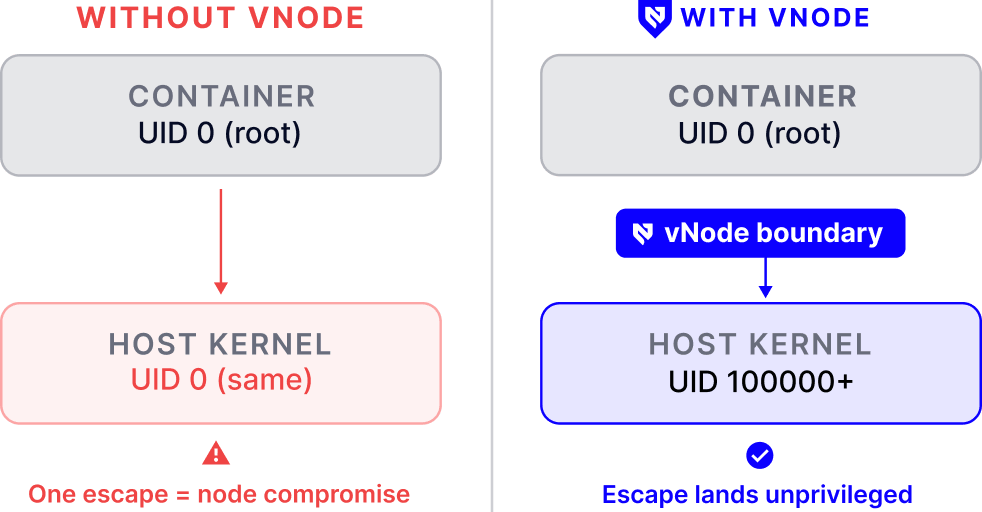
vNode uses Linux user namespaces and seccomp to restrict workload privileges and system calls. It adds runtime hardening for distributed GPU infrastructure without a guest kernel or hypervisor, complementing dedicated workers rather than allocating GPUs.
Linux user namespaces and seccomp
No guest kernel or hypervisor
Helps limit workload breakout
AI Workload Integration
Supported AI Workload Templates
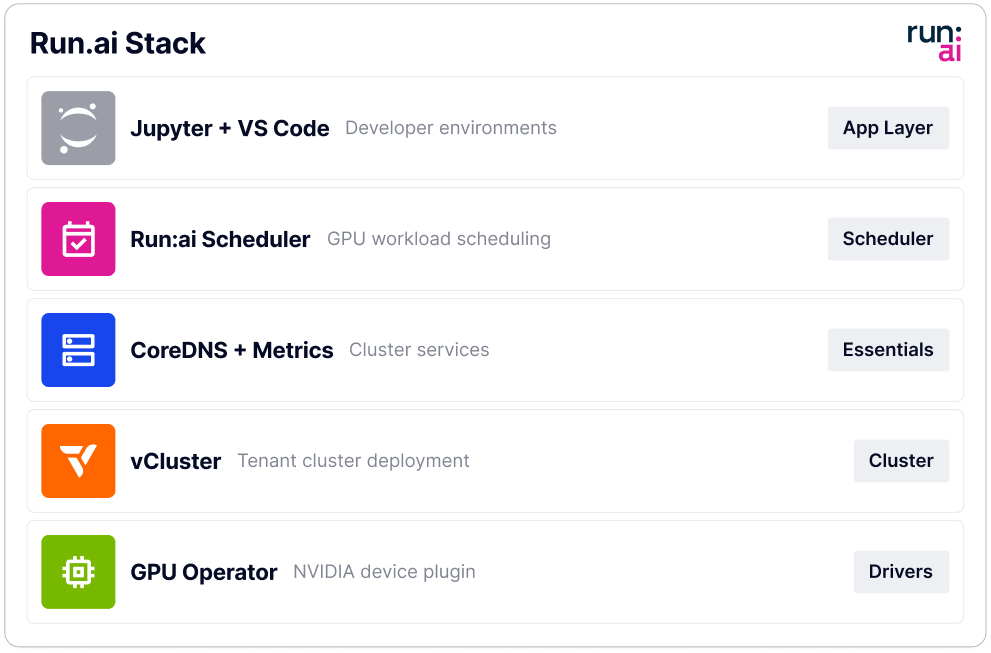
Use supported workload templates for distributed GPU infrastructure, including the NVIDIA Run:AI partner integration. Configure GPU, network and storage prerequisites, and validate the selected template for Private Nodes before offering it to production customers.
Native NVIDIA Run:AI catalog
Validate Private Node configuration
Release-specific integration prerequisites