platform-eng

Managed Slurm Infrastructure with Dedicated Tenant Workers

Plan dedicated infrastructure for managed Slurm services. vMetal provisions machines, and vCluster supplies Kubernetes tenant environments with Private Nodes; packaged managed Slurm remains planned.

Trusted by the fastest-growing AI cloud providers
Problem

Why Managed Slurm Is Hard

GPU infrastructure that serves many Slurm customers needs isolation at both the control plane and the worker layer.

Weak Tenant Boundaries

Namespace-only designs share control-plane and node-level components, which is a poor fit for untrusted or external tenants.

Slow, Expensive Provisioning

Building a separate infrastructure stack for every tenant adds provisioning work and creates more systems to operate.

Operational Complexity at Scale

Without a central management plane, templates, access, observability, and lifecycle operations drift across tenant environments.

Solution

Dedicated Infrastructure for Slurm Evaluation

vMetal and vCluster provide machine orchestration and dedicated Kubernetes tenant infrastructure through Private Nodes. Slurm retains job scheduling responsibility; upstream Slinky can be evaluated separately while the packaged managed Slurm offering remains planned. Lintasarta runs 170+ tenant clusters in production.

Foundations for a Slurm Tenant Environment

Plan tenant worker capacity, network boundaries and recovery responsibilities for an upstream Slurm operator evaluation.

Certified Stacks

Versioned Tenant Application Templates

Certified Stacks provide versioned application deployments. For Slurm evaluation, distinguish Slinky reference implementations from an available packaged managed service. Validate the selected stack, release and Private Node configuration; packaged managed Slurm remains planned.

  • Versioned application configuration
  • Validate selected stack and release
  • Separate managed Slurm availability
Worker Isolation

Private Nodes for Slurm Evaluation

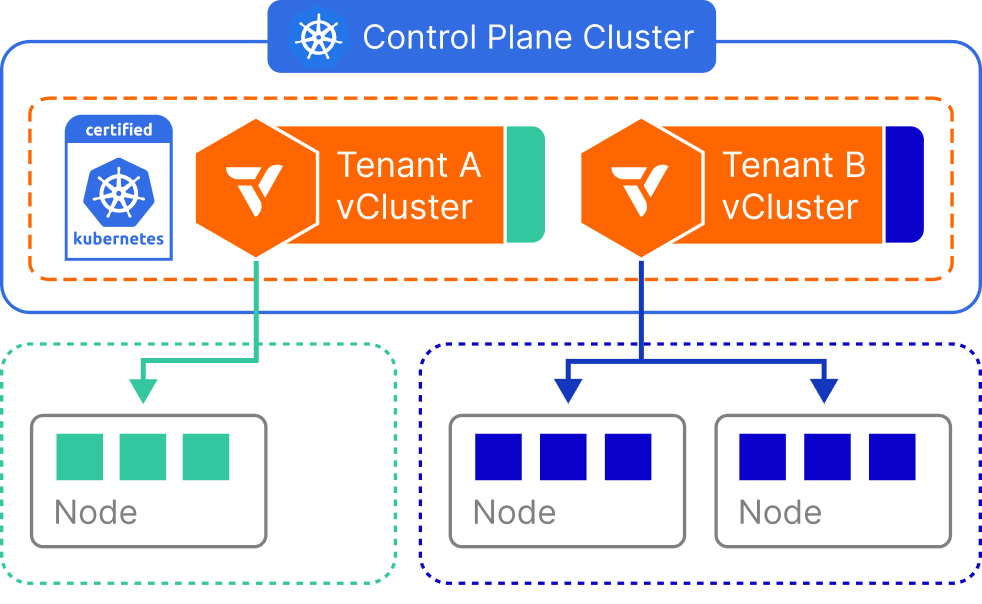
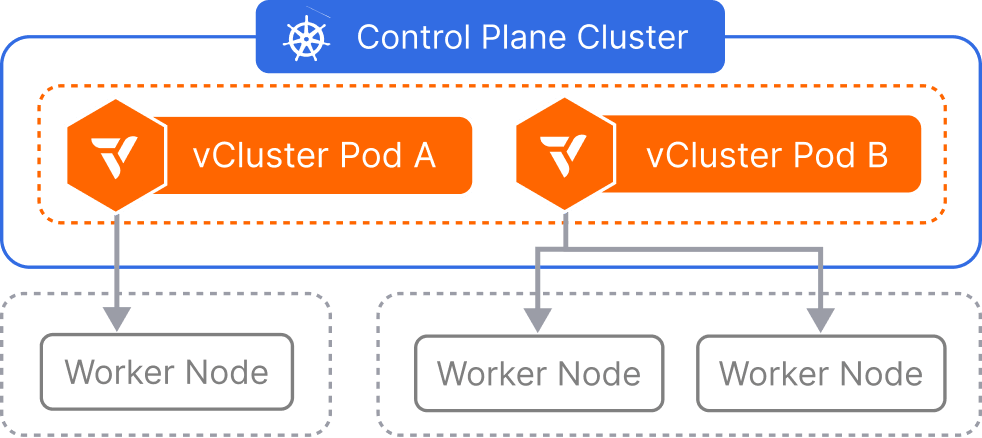
Private Nodes dedicate worker capacity to one tenant cluster, with its own CNI and storage configuration. For Slurm infrastructure planning, select physical servers or VMs according to the required infrastructure boundary.

  • Dedicated worker nodes per tenant
  • Tenant-owned CNI and storage configuration
  • Physical servers or supported VMs
Control Plane

Kubernetes Control Planes for Slurm Evaluation

Each Kubernetes tenant environment has an independent API, backing store and RBAC scope. This supplies the control-plane foundation for a Slurm operator evaluation; the operator and Slurm components have separate deployment and scheduling responsibilities.

  • Independent tenant API and data store
  • Tenant-scoped scheduling on Private Nodes
  • No dedicated control-plane servers per tenant
Network Isolation

Hardware-Enforced Tenant Networking

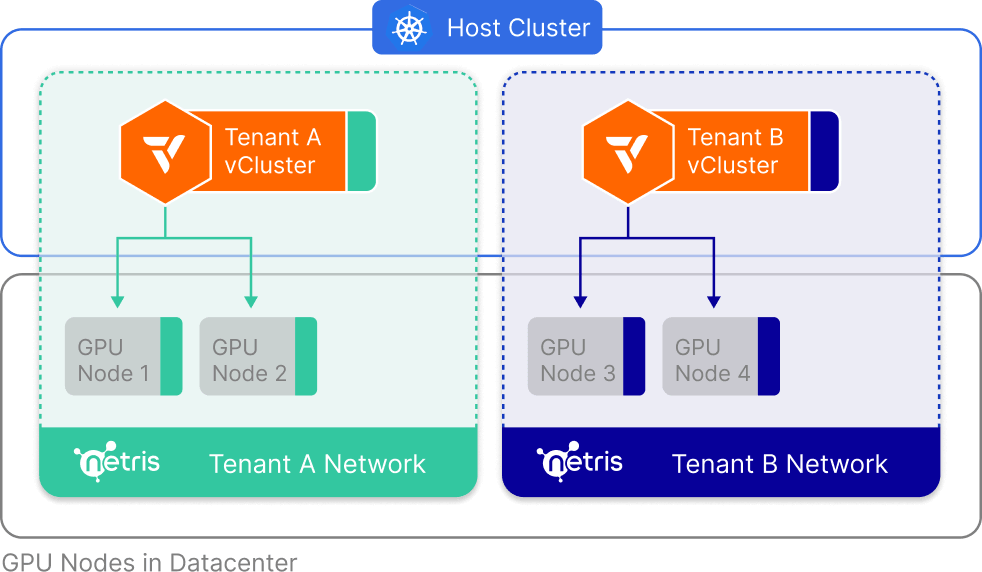
Tenant-owned CNI configuration and supported Netris integrations provide separate network controls for Slurm infrastructure planning. Ethernet segmentation can use VLANs, VRFs and ACLs; InfiniBand isolation uses fabric partitions rather than Ethernet constructs.

  • Tenant-owned worker network configuration
  • Netris integration for supported fabrics
  • Explicit segmentation and access policies
Operations

Snapshots and Recovery Workflows

Use tenant control-plane snapshots and documented backup workflows for Slurm infrastructure planning. Combine these with monitoring integrations and separate workload-data protection; recovery planning must include persistent volumes, connected infrastructure and restore testing.

  • Tenant control-plane snapshots
  • Separate workload-data backups
  • Documented restore procedures

Why vCluster

This isn’t a side project. Behind every vCluster deployment is 5+ years of deep K8s engineering, security hardening, and battle-tested infrastructure work at massive scale.

100K+
GPUs Powered
50+
GPU Clouds & F500s
<45
Days to Launch
30K
GitHub Stars

Get Started in 3 Steps

1
Schedule a Demo

Talk to our team about your stack

2
Deploy vCluster

Deploy vCluster on your infra in minutes

3
Onboard Your Tenants

Go live with a hyperscaler-grade tenant experience in days

FAQs

Is packaged managed Slurm available on vCluster Platform?

The public vCluster roadmap lists the packaged Slurm platform as planned. Today, distinguish that future offering from evaluating upstream Slinky inside a Kubernetes tenant environment. vMetal can supply infrastructure and Private Nodes can dedicate workers, but operator setup, job scheduling, compatibility validation and support responsibilities remain separate from provisioning a tenant cluster.

How does vCluster isolate Slurm tenants?

vCluster gives each tenant an independent Kubernetes API, data store and RBAC scope. Private Nodes dedicate worker capacity to that tenant, including its own CNI and storage configuration. vMetal orchestrates the machines underneath. This separates tenant administration and worker placement; shared infrastructure, application permissions and network policies still require an explicit security design.

Can I evaluate Slurm alongside Kubernetes workloads?

Teams can evaluate upstream Slinky within a Kubernetes tenant environment on dedicated workers. That is different from offering a supported packaged managed Slurm product through vCluster. Keep capacity allocation, operator configuration and support responsibilities explicit, and validate how Slurm jobs access GPU resources. The public vCluster roadmap still lists its packaged Slurm platform as planned.

What determines readiness for a Slurm tenant environment?

A tenant Kubernetes control plane is only the infrastructure starting point. Slurm readiness also needs a configured operator, dedicated workers, storage, networking, GPU drivers and tested job execution. Provisioning time depends on available inventory and infrastructure drivers. The packaged vCluster managed Slurm offering remains planned, so a Kubernetes provisioning estimate is not a managed Slurm launch promise.

Does vCluster support air-gapped or compliance-sensitive Slurm deployments?

Supported plans include air-gapped deployment and FIPS features. Private Nodes, tenant-scoped access and optional network segmentation provide controls you can include in a regulated deployment. Select supported images and configurations, and validate the full environment against your requirements. These capabilities do not establish certification of the customer's service, application, hardware or operational procedures.

What infrastructure can host a Slurm operator evaluation?

A Kubernetes tenant environment can use dedicated bare metal workers or supported VM workers through Private Nodes. For an upstream Slurm operator evaluation, choose hardware and GPU access that meet the operator and workload requirements. vMetal can orchestrate supported provisioning after driver setup. Validate the full Slurm configuration separately; machine readiness does not establish a supported packaged managed service.

Plan Dedicated Slurm Infrastructure

Discuss dedicated tenant infrastructure and the requirements for evaluating Slurm operators.