ai-cloud
Build Your AI Cloud on Hard Tenant Isolation
Turn GPU infrastructure into an AI cloud. vMetal orchestrates machines, and vCluster provides independent tenant clusters with dedicated Private Nodes and optional workload isolation.
Turn GPU infrastructure into an AI cloud. vMetal orchestrates machines, and vCluster provides independent tenant clusters with dedicated Private Nodes and optional workload isolation.
AI cloud providers face three compounding problems that delay revenue and erode margins.
Selling bare metal GPUs alone is a race to the bottom. Customers expect managed environments and self-service, and they compare you with the hyperscalers.
Building a GPU cloud platform in-house requires significant engineering investment.
Namespace isolation is too weak, and separate physical clusters are too expensive. Standard Kubernetes forces you to pick one.
vMetal orchestrates bare metal and VM capacity through one Machine API. vCluster provisions independent Kubernetes tenant environments with dedicated Private Nodes, while teams add supported workload stacks. vCluster Labs serves 50+ GPU clouds & Fortune 500s.
Every layer of the stack purpose-built for GPU cloud operators who need tenant isolation without sacrificing bare metal performance.
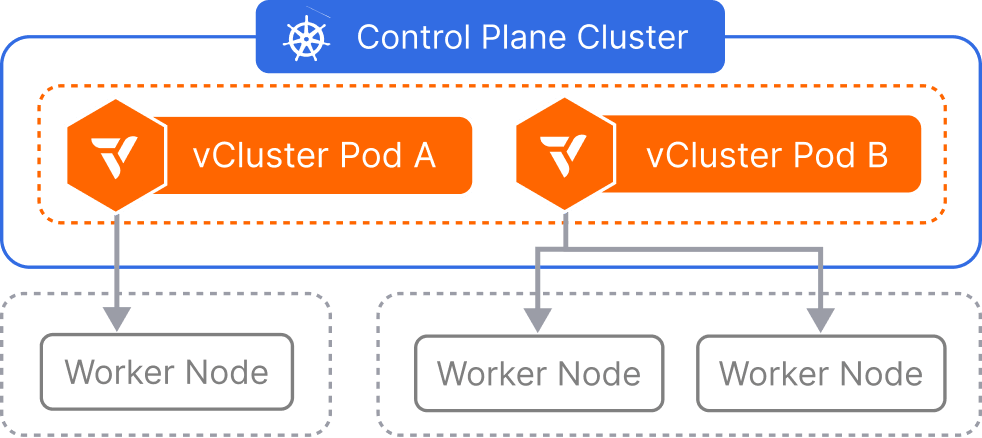
Each tenant has an independent Kubernetes API, data store and RBAC boundary. Lightweight control-plane hosting reduces dedicated server requirements for AI cloud services; Private Nodes keep production workers tenant-specific.
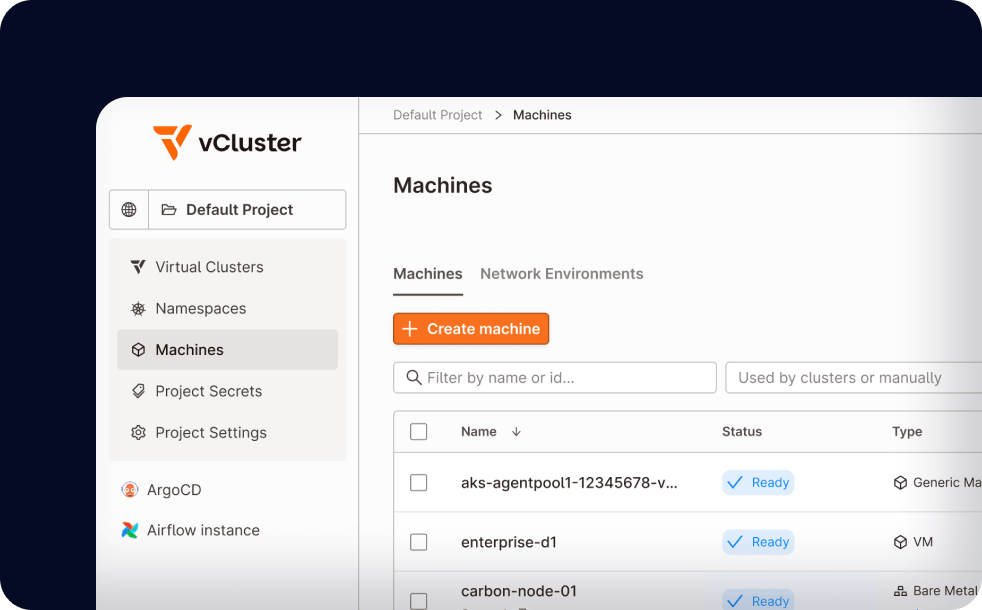
vMetal exposes one Machine API above bare metal and VM provisioning drivers. Registered inventory, images and credentials enable repeatable machine lifecycle workflows for AI cloud services. Network automation uses supported integrations such as Netris.
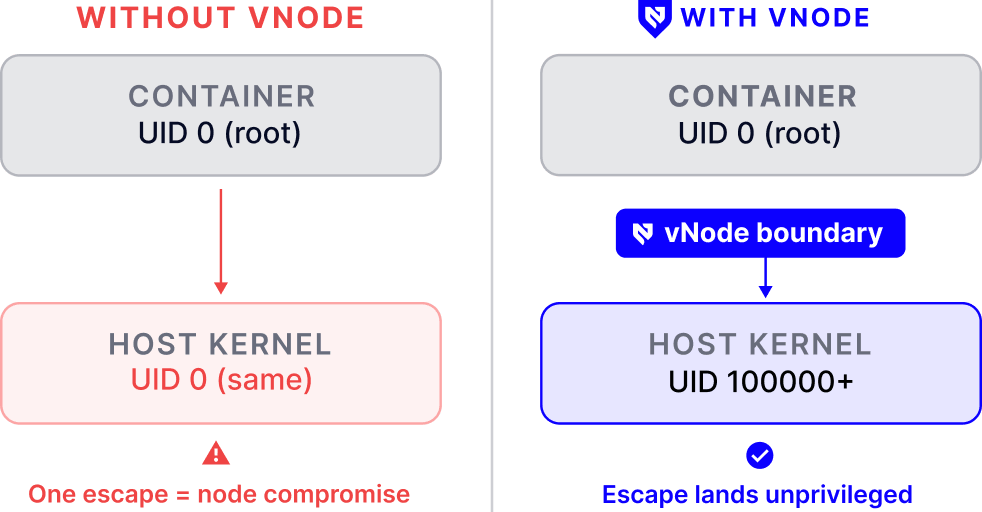
vNode uses Linux user namespaces and seccomp to restrict workload privileges and system calls. It adds runtime hardening for AI cloud services without a guest kernel or hypervisor, complementing dedicated workers rather than allocating GPUs.
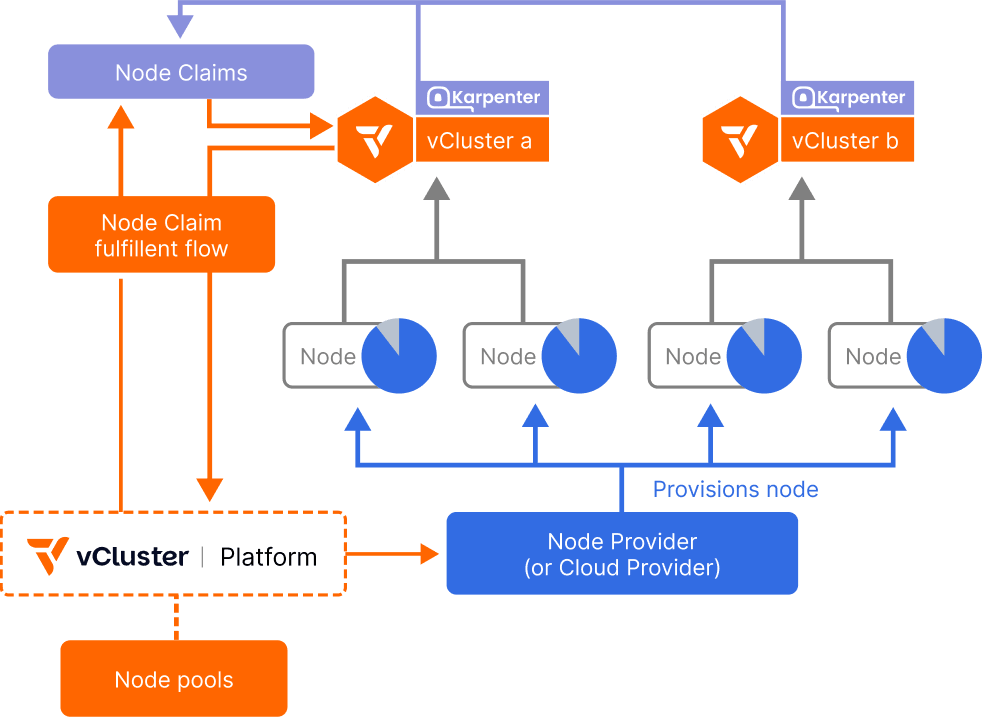
Karpenter-based Auto Nodes requests worker capacity according to configured policies. With the vMetal provider, Machine requests provision available infrastructure for AI cloud services; inventory, driver readiness and release rules determine actual capacity.
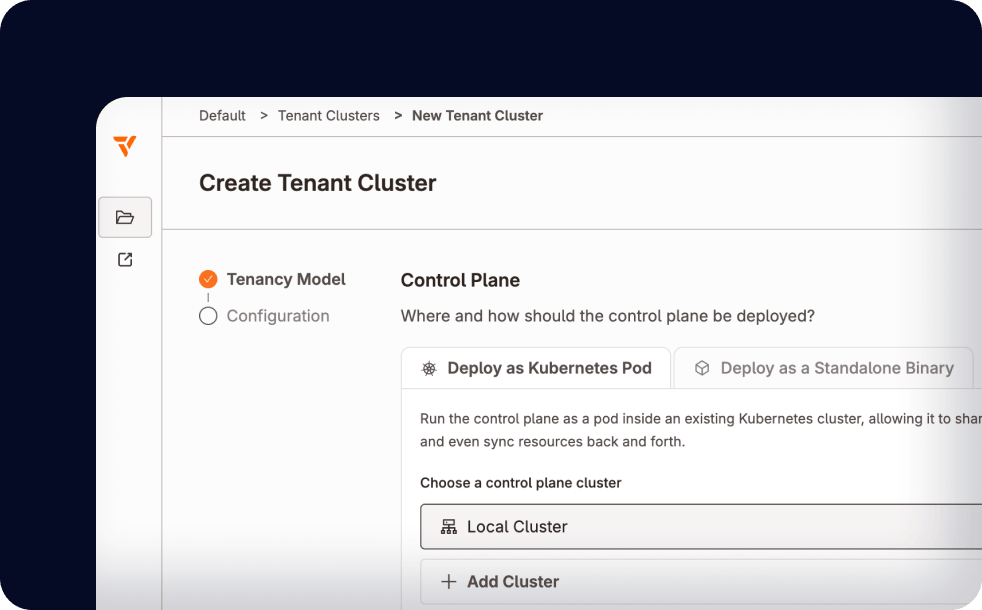
Give your AI cloud customers a self-service portal to provision and manage their own Kubernetes environments. Deliver the cloud experience AI teams expect from hyperscalers, on your infrastructure.
This isn’t a side project. Behind every vCluster deployment is 5+ years of deep K8s engineering, security hardening, and battle-tested infrastructure work at massive scale.
Talk to our team about your stack
Deploy vCluster on your infra in minutes
Go live with a hyperscaler-grade tenant experience in days
Operators expose approved Kubernetes templates through vCluster Platform interfaces or an integrated customer portal. Templates define supported configurations, while access and capacity policies govern requests. vMetal can provision machines and Private Nodes dedicate production workers. Customers receive their own Kubernetes environment once its control plane, networking, storage and worker capacity are ready; application stacks have additional prerequisites.
vCluster virtualizes the Kubernetes control plane. Each tenant receives a cluster with its own API server, data store, scheduler, and RBAC running as a lightweight pod inside the control plane cluster, which gives tenants cluster-admin rights without a dedicated physical cluster each. Private Nodes, the recommended production model, add dedicated worker nodes with hardware-level separation. vNode can add workload-level isolation, and Shared Nodes remain available for your own internal dev, test, and CI/CD.
Boost Run went from decision to production launch in under 45 days on vCluster, and Lintasarta runs 170+ tenant clusters in production. The time saved comes from running a production-proven stack for bare metal provisioning, tenant cluster orchestration, and Day 2 operations instead of building one yourself.
vCluster Standalone runs as a Kubernetes binary directly on Linux without requiring another Kubernetes cluster, k3s or kubeadm. It can provide an initial Kubernetes foundation. vMetal is a separate infrastructure orchestration layer that requires vCluster Platform and a connected Kubernetes cluster for its Metal3/Ironic path. Hardware registration, images, credentials and driver setup remain prerequisites for machine provisioning.
vNode uses Linux user namespaces and seccomp to restrict workload privileges and system calls, helping prevent container breakout. It uses the underlying Linux kernel rather than a separate guest kernel. Add it as runtime hardening alongside dedicated Private Nodes, patching and least-privilege policies. Validate kernel, container runtime, GPU access and workload compatibility; it is not a replacement for GPU allocation or application authorization.
vCluster Labs software powers 100K+ GPUs and 1M+ CPUs, serving 50+ GPU clouds & Fortune 500s combined. In production, Lintasarta operates 170+ tenant clusters, while Boost Run completed its managed Kubernetes launch in under 45 days from the decision. These named deployments provide scale and launch examples for teams evaluating the platform for their own infrastructure.
See how AI cloud providers run isolated tenant clusters on bare metal GPUs with vCluster.
