ai-cloud
NVIDIA DGX Kubernetes for AI Cloud Providers
Turn NVIDIA DGX capacity into isolated tenant environments. vMetal orchestrates machine provisioning, and vCluster pairs separate tenant control planes with dedicated DGX Private Nodes.
Turn NVIDIA DGX capacity into isolated tenant environments. vMetal orchestrates machine provisioning, and vCluster pairs separate tenant control planes with dedicated DGX Private Nodes.
Common barriers blocking AI cloud providers from monetizing NVIDIA DGX infrastructure.
Namespace isolation is too weak. Separate physical clusters per tenant make NVIDIA DGX Kubernetes economics unworkable at scale.
AI teams have used AWS and GCP. They expect self-service environments and managed Kubernetes, and they will leave if you cannot deliver.
Building a GPU cloud platform in-house takes significant engineering investment, and the DGX hardware sits underused while you build it.
vMetal orchestrates DGX machine provisioning through configured infrastructure drivers. vCluster runs separate Kubernetes tenant control planes and attaches dedicated DGX Private Nodes, with tenant-owned network and storage configuration. vCluster Labs serves 50+ GPU clouds & Fortune 500s.
From bare metal provisioning to tenant isolation and workload security, every layer of the DGX Kubernetes stack is covered.
vMetal exposes one Machine API above bare metal and VM provisioning drivers. Registered inventory, images and credentials enable repeatable machine lifecycle workflows for DGX tenant environments. Network automation uses supported integrations such as Netris.
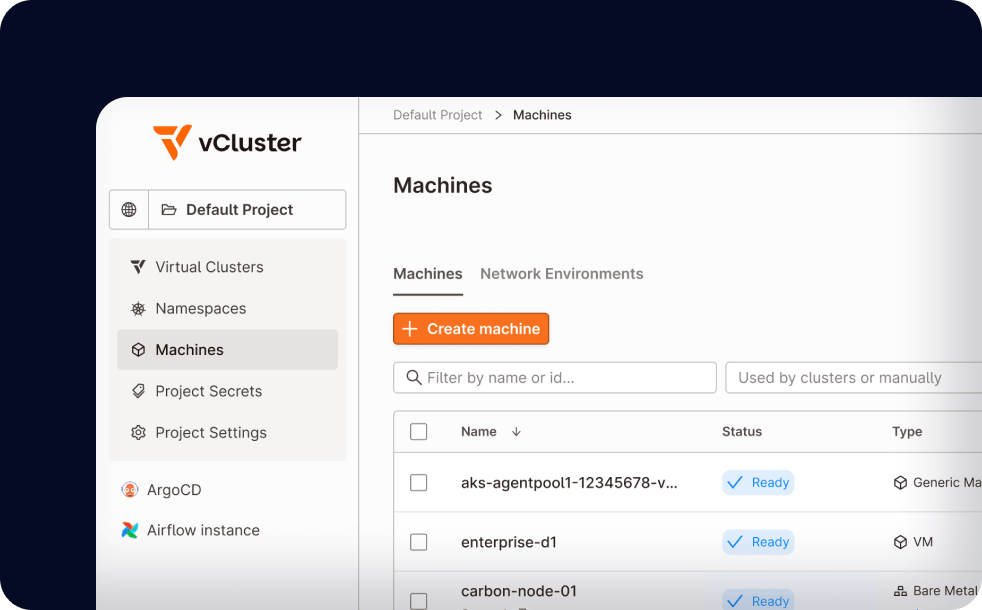
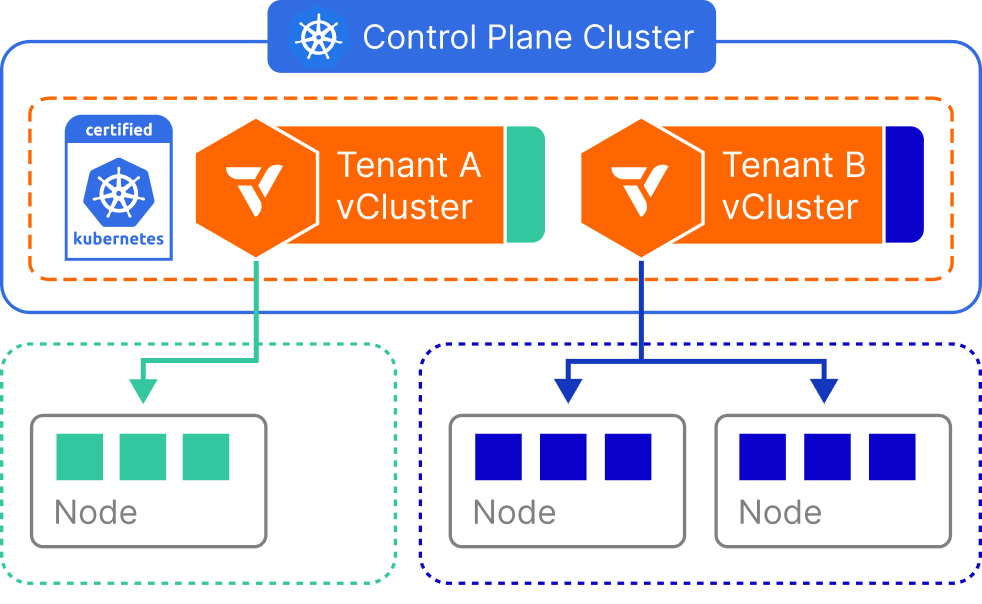
Each tenant has an independent Kubernetes API, data store and RBAC boundary. Lightweight control-plane hosting reduces dedicated server requirements for DGX tenant environments; Private Nodes keep production workers tenant-specific.
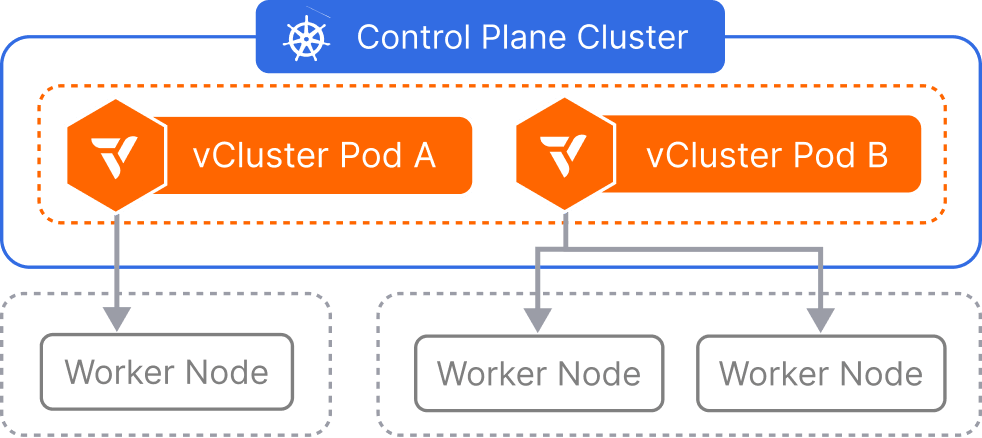
Private Nodes dedicate worker capacity to one tenant cluster, with its own CNI and storage configuration. For DGX tenant environments, select physical servers or VMs according to the required infrastructure boundary.
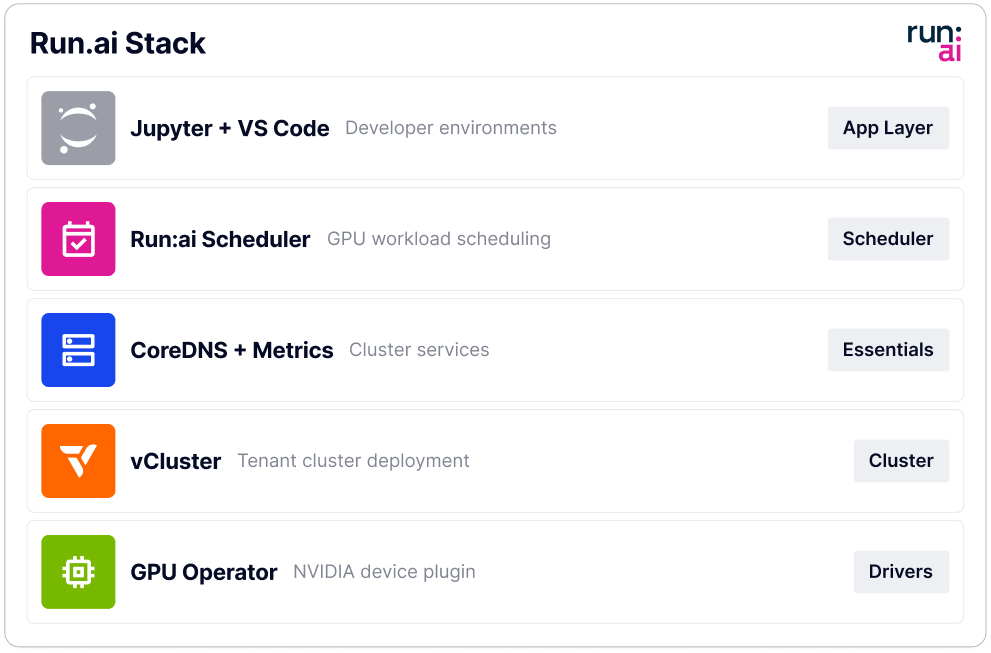
Use supported workload templates for DGX tenant environments, including the NVIDIA Run:AI partner integration. Configure GPU, network and storage prerequisites, and validate the selected template for Private Nodes before offering it to production customers.
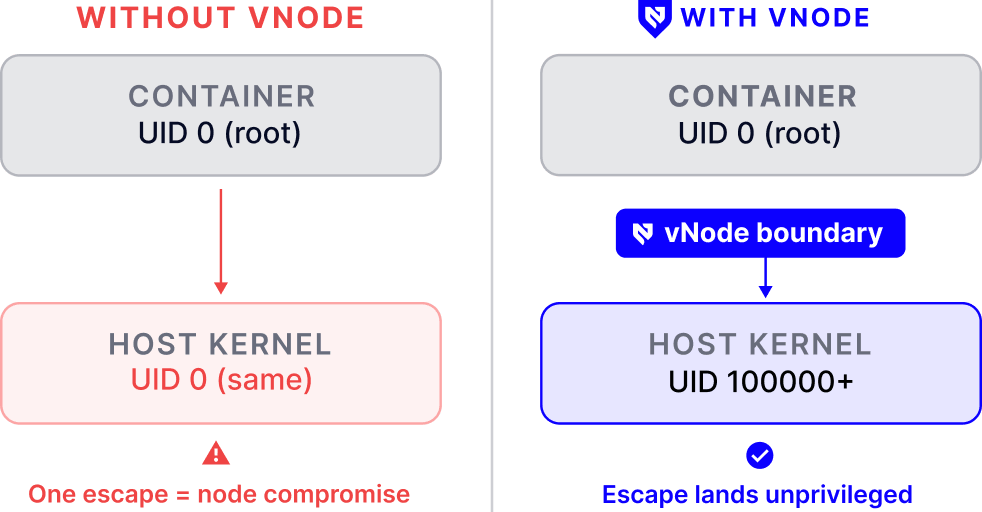
vNode uses Linux user namespaces and seccomp to restrict workload privileges and system calls. It adds runtime hardening for DGX tenant environments without a guest kernel or hypervisor, complementing dedicated workers rather than allocating GPUs.
This isn’t a side project. Behind every vCluster deployment is 5+ years of deep K8s engineering, security hardening, and battle-tested infrastructure work at massive scale.
Talk to our team about your stack
Deploy vCluster on your infra in minutes
Go live with a hyperscaler-grade tenant experience in days
Private Nodes are worker nodes joined to one tenant cluster, with that tenant's own CNI and storage configuration. They can be physical machines or supported VMs. Use dedicated bare metal when the service requires exclusive physical servers. vMetal can provision the underlying machines, while platform policies define which capacity a tenant may request and how it is released.
vCluster Labs software powers 100K+ GPUs and 1M+ CPUs, serving 50+ GPU clouds & Fortune 500s combined. In production, Lintasarta operates 170+ tenant clusters, while Boost Run completed its managed Kubernetes launch in under 45 days from the decision. These named deployments provide scale and launch examples for teams evaluating the platform for their own infrastructure.
Dedicated Private Nodes remove cross-tenant workload placement from those workers. Bare metal avoids a hypervisor layer, but this is not a throughput or latency guarantee. GPU drivers, workload configuration, network fabrics and storage can still influence performance. vNode adds runtime hardening using the Linux kernel; benchmark the selected stack against the workload and service levels you intend to offer.
Boost Run went from decision to production launch in under 45 days for its managed Kubernetes service. That is a customer example rather than a promised implementation time. Your launch depends on machine inventory, driver configuration, networking, storage, templates and service integrations. vMetal and vCluster connect machine orchestration with tenant cluster delivery, reducing the infrastructure workflows you need to build yourself.
vCluster gives each tenant an independent Kubernetes API, data store and RBAC scope. Private Nodes dedicate worker capacity to that tenant, including its own CNI and storage configuration. vMetal orchestrates the machines underneath. This separates tenant administration and worker placement; shared infrastructure, application permissions and network policies still require an explicit security design.
Supported plans include air-gapped deployment and FIPS features. Private Nodes, tenant-scoped access and optional network segmentation provide controls you can include in a regulated deployment. Select supported images and configurations, and validate the full environment against your requirements. These capabilities do not establish certification of the customer's service, application, hardware or operational procedures.
See how vCluster powers isolated tenant clusters on bare metal DGX infrastructure.
