platform-eng

Rancher Alternative for GPU Cluster Management

Evaluate a Rancher alternative for customer-facing GPU infrastructure. vMetal orchestrates machine provisioning, and vCluster gives production tenants separate control planes and dedicated Private Nodes.

Trusted by the fastest-growing AI cloud providers
Problem

What GPU Teams Run Into

Teams running GPU workloads for many tenants tend to hit the same walls, whatever tool manages their clusters.

Namespace Isolation Is Too Weak

Without careful RBAC configuration, namespace isolation can expose platform internals, including cluster-wide agents and potentially other tenants' nodes and pods.

Separate Clusters Are Too Expensive

Provisioning a full physical cluster per tenant creates cost and operational overhead that makes scaling unviable.

Infrastructure Workflows Remain Disconnected

Machine provisioning, tenant cluster delivery and ongoing operations need a connected workflow with explicit ownership at each layer.

Solution

A Rancher Alternative Built for GPU Infrastructure

vCluster combines separate Kubernetes tenant control planes with dedicated Private Nodes. vMetal orchestrates infrastructure, and Platform provides fleet templates, access control and tenant operations. vCluster Labs serves 50+ GPU clouds & Fortune 500s.

Built for High-Density GPU Workloads

Every layer, from bare metal provisioning to workload isolation, is built around lightweight, isolated tenant environments.

Tenant Isolation

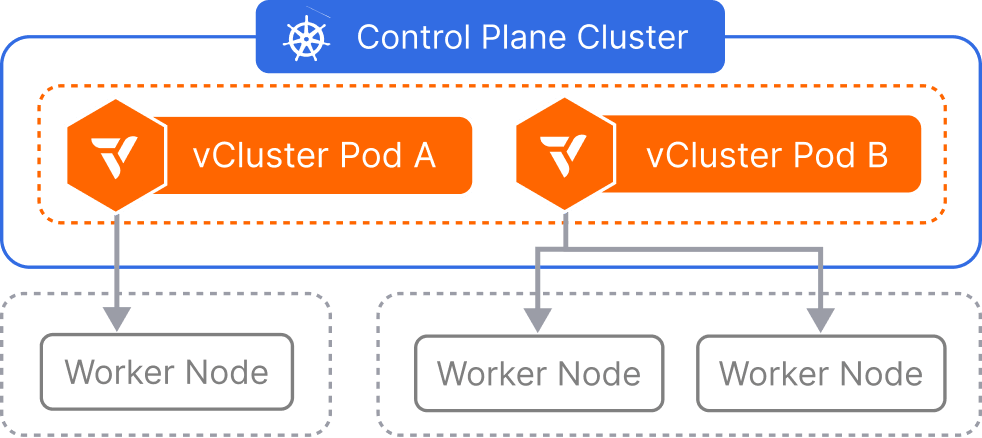
Isolated Tenant Clusters as Lightweight Pods

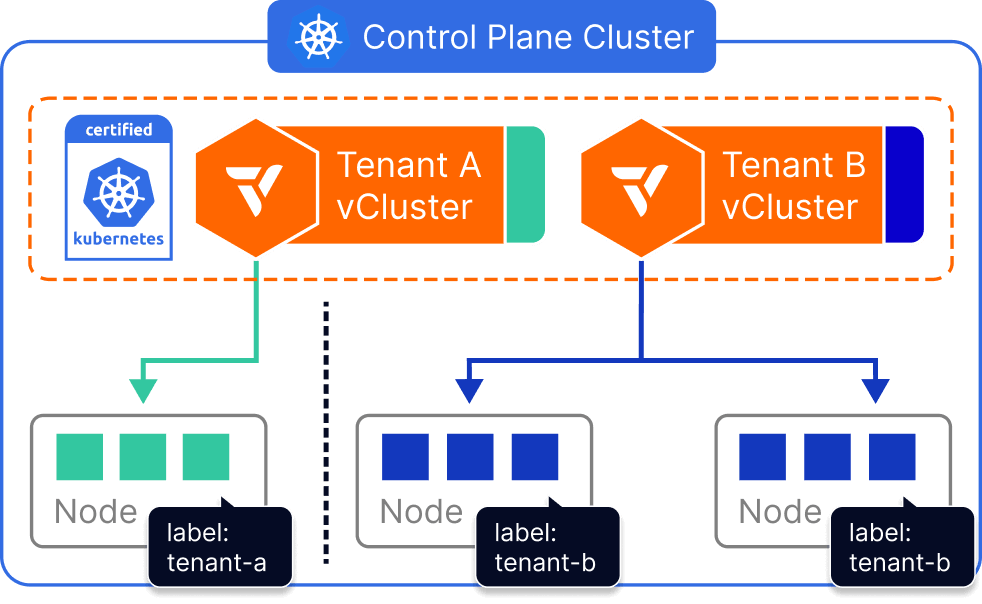
Each tenant has an independent Kubernetes API, data store and RBAC boundary. Lightweight control-plane hosting reduces dedicated server requirements for customer GPU infrastructure; Private Nodes keep production workers tenant-specific.

  • Independent tenant API and data store
  • Tenant-scoped scheduling on Private Nodes
  • No dedicated control-plane servers per tenant
Platform Operations

Central Fleet Management Across All Clusters

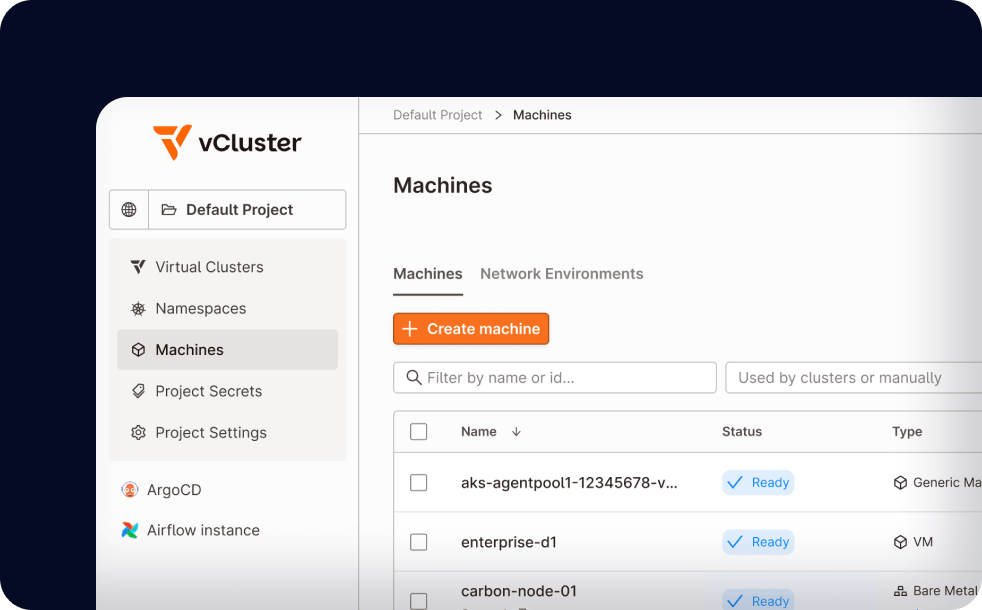
Coordinate tenant environments for customer GPU infrastructure through one UI, CLI and API. Templates, access policies and quotas provide central operator controls while tenant Kubernetes APIs and dedicated production workers remain separate.

  • Single pane across all tenant clusters
  • SSO, quotas, and templates included
  • CLI and API for full automation
Day 2 Operations

Snapshots and Recovery Workflows

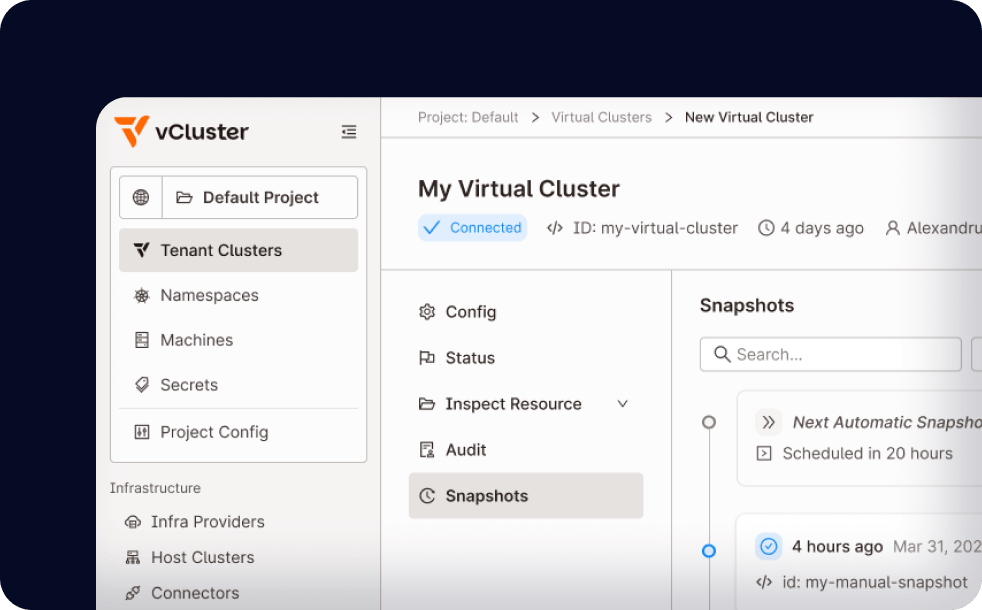
Use tenant control-plane snapshots and documented backup workflows for customer GPU infrastructure. Combine these with monitoring integrations and separate workload-data protection; recovery planning must include persistent volumes, connected infrastructure and restore testing.

  • Tenant control-plane snapshots
  • Separate workload-data backups
  • Documented restore procedures
Node Isolation

Private Nodes Dedicate Tenant GPU Workers

Dedicate GPU workers to each tenant through Private Nodes. This removes cross-tenant workload placement from those workers for customer GPU infrastructure; network bandwidth, storage and GPU partitioning still need explicit policies.

  • Dedicated worker nodes per tenant
  • Tenant-owned CNI and storage configuration
  • Physical servers or supported VMs
AI Workload Integration

Supported AI Workload Templates

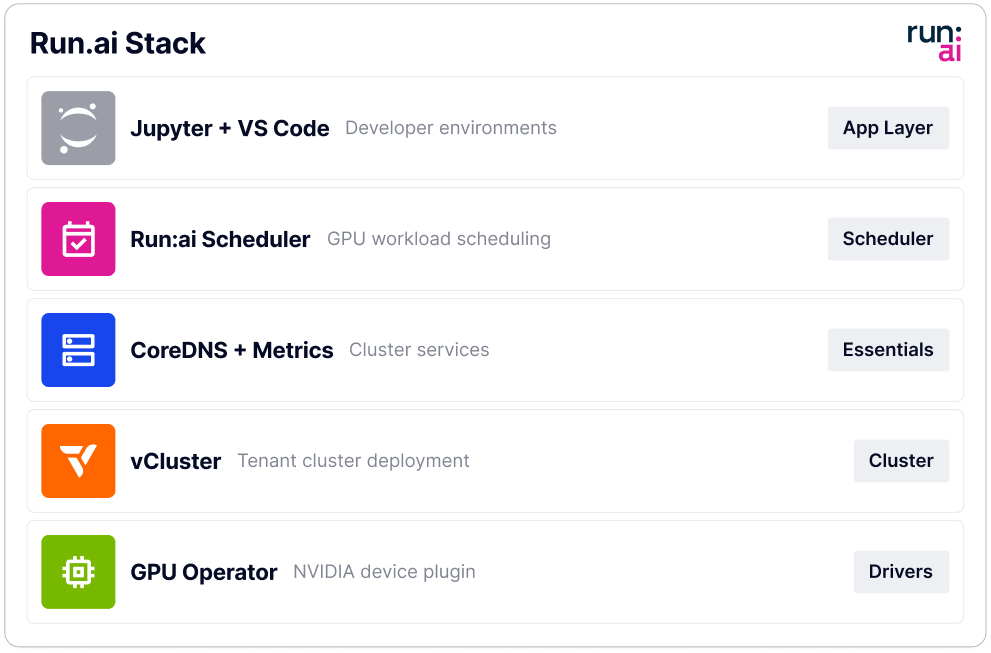
Use supported workload templates for customer GPU infrastructure, including the NVIDIA Run:AI partner integration. Configure GPU, network and storage prerequisites, and validate the selected template for Private Nodes before offering it to production customers.

  • Native NVIDIA Run:AI catalog
  • Validate Private Node configuration
  • Release-specific integration prerequisites
Why vCluster

This isn’t a side project. Behind every vCluster deployment is 5+ years of deep K8s engineering, security hardening, and battle-tested infrastructure work at massive scale.

100K+
GPUs Powered
50+
GPU Clouds & F500s
<45
Days to Launch
30K
GitHub Stars

Get Started in 3 Steps

1
Schedule a Demo

Talk to our team about your stack

2
Deploy vCluster

Deploy vCluster on your infra in minutes

3
Onboard Your Tenants

Go live with a hyperscaler-grade tenant experience in days

FAQs

What does vCluster offer teams evaluating a Rancher alternative?

Evaluate vCluster against the service you need to deliver: separate tenant Kubernetes APIs, dedicated production workers and infrastructure lifecycle operations. Private Nodes provide the recommended customer worker model, while vMetal orchestrates machines and Platform coordinates templates and access. Compare documented versions and configurations directly; an embedded runtime alone does not describe every capability of another vendor's platform.

Does vCluster support standard Kubernetes APIs?

vCluster is a CNCF-certified Kubernetes distribution and exposes standard Kubernetes APIs in tenant environments. This supports familiar clients, Helm charts and cluster-scoped resources such as CRDs. Certification covers Kubernetes conformance rather than an entire AI platform or customer deployment. Validate the selected version, networking, storage, GPU drivers and runtime integrations for the workloads you plan to support.

Which tenant boundaries does vCluster provide?

vCluster gives each tenant an independent Kubernetes API, data store and RBAC scope. Private Nodes dedicate worker capacity to that tenant, including its own CNI and storage configuration. vMetal orchestrates the machines underneath. This separates tenant administration and worker placement; shared infrastructure, application permissions and network policies still require an explicit security design.

Can vCluster replace Rancher for bare metal GPU infrastructure?

vMetal exposes a stable Machine API above infrastructure-specific drivers for bare metal and VMs. Drivers handle supported provisioning mechanics such as imaging, registration and cleaning. Operators configure inventory, credentials and images before automation runs. vCluster can then use provisioned machines as dedicated Private Nodes, connecting the infrastructure lifecycle to the tenant cluster that needs the capacity.

How quickly can teams migrate from Rancher to vCluster?

Standard Kubernetes APIs support familiar deployment tools, but migration still requires validation of storage, networking, identity, GPU drivers and runtime-dependent operators. Create a tenant cluster with the required Private Nodes configuration, test representative workloads, and plan data movement and rollback before switching traffic. Boost Run's launch timeline is not a migration estimate for your existing environment.

What recovery workflows does vCluster support?

Tenant control-plane snapshots and documented backup and restore workflows support recovery planning. They do not replace backups of persistent volumes, application data or connected infrastructure. Define monitoring, upgrade and restore procedures for the chosen worker model and test them against your recovery objectives. Private Node clusters do not support workload or control-plane auto-sleep, so capacity release needs separate policies.

Scale GPU Infrastructure With vCluster

See how vCluster delivers tenant isolation and fleet management built for GPU scale.