ai-cloud

GPU Cluster Isolation for AI Clouds

GPU cluster isolation means each tenant's jobs, data and control plane stay apart from every other tenant on the fleet. vCluster isolates the control plane, Private Nodes isolate the workers, and Netris can carry the boundary into the physical network.

Trusted by the fastest-growing AI cloud providers
Problem

Why Generic Isolation Fails at Scale

GPU tenant isolation needs clear boundaries at the control plane, worker node, and network layers.

Namespace Isolation Is Too Weak

Namespace-only designs share control-plane and node-level components between tenants.

Separate Clusters Are Too Expensive

Running a separate management stack for every tenant increases infrastructure and operational work.

No Control Plane Boundaries

A shared API server and RBAC model cannot provide the same tenant control-plane boundary as a dedicated tenant cluster.

Solution

Layered Tenant Isolation From Control Plane to Kernel

vCluster gives every tenant its own virtualized control plane and uses Private Nodes as the production default. Optional vNode and Netris integrations strengthen the runtime and physical network boundaries.

Full-Stack GPU Cluster Tenant Isolation

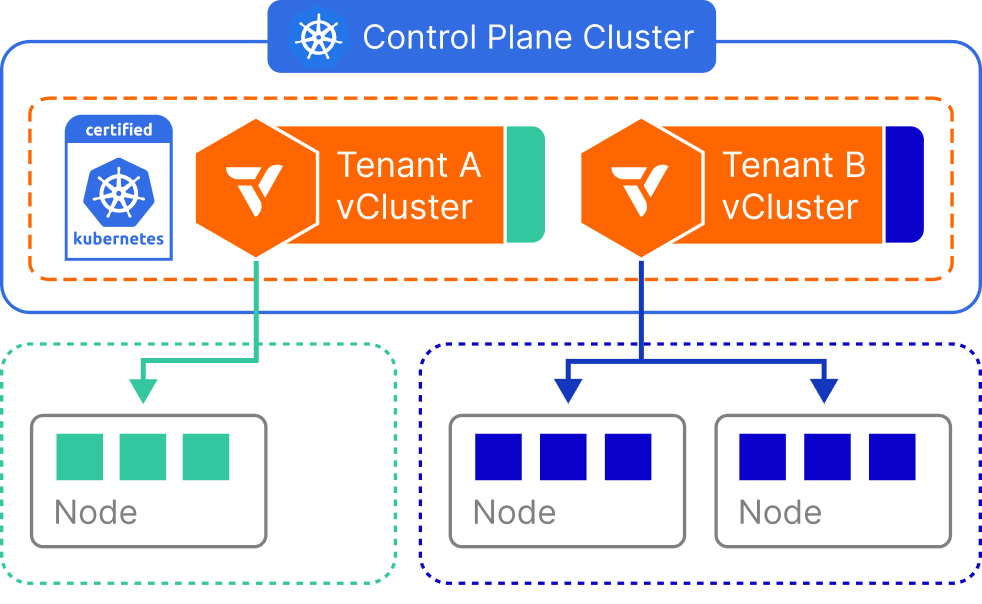
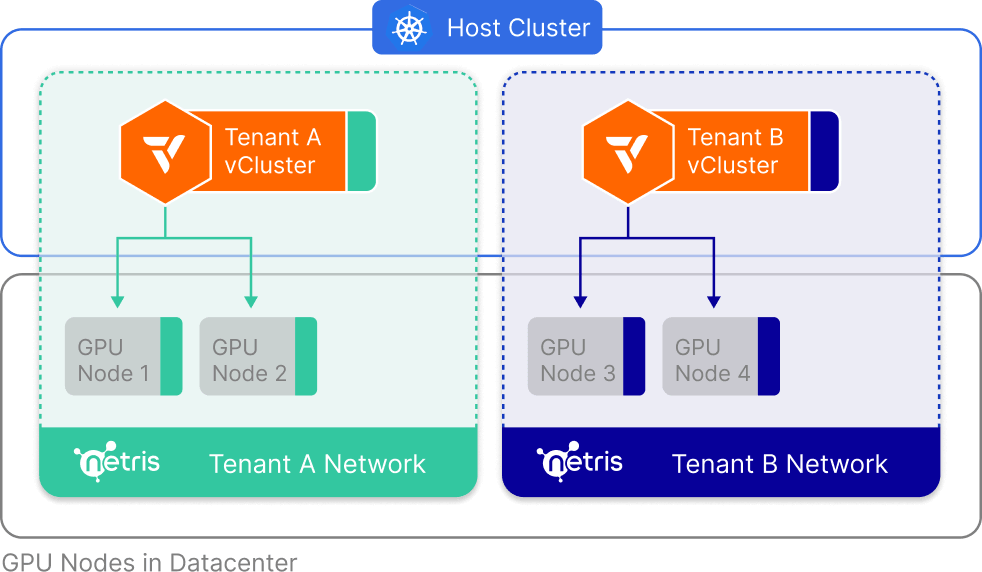
GPU cluster isolation spans the tenant control plane, dedicated Private Nodes, optional runtime isolation, and optional hardware network isolation.

Hardware Isolation

Private Nodes Per Tenant Cluster

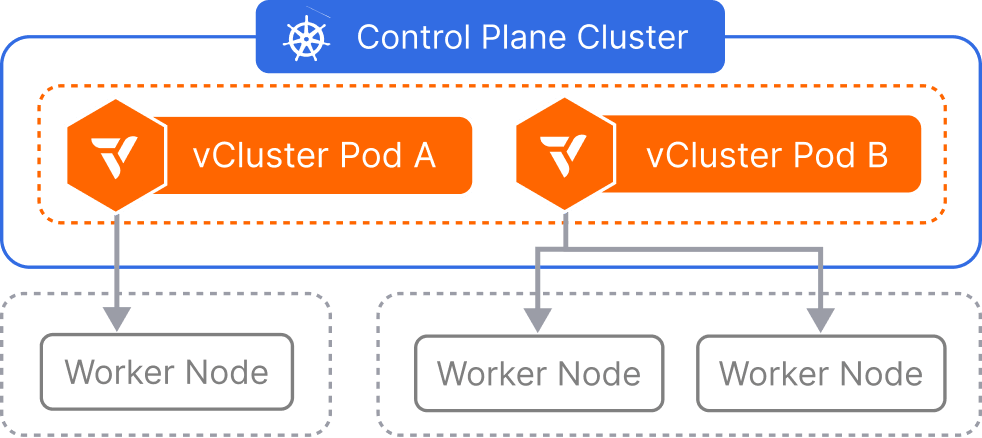
Private Nodes assign dedicated worker nodes with tenant-scoped networking and storage to each production tenant cluster.

  • Per-tenant CNI and storage
  • No cross-tenant workload placement
  • Hardware-level security boundary
Control Plane

Virtualized Control Planes Per Tenant

Each tenant receives its own virtualized Kubernetes control plane, API server, and RBAC boundary.

  • Own API server and etcd per tenant
  • Lightweight control plane
  • Isolated blast radius per tenant
Workload Security

Kernel-Native Workload Isolation

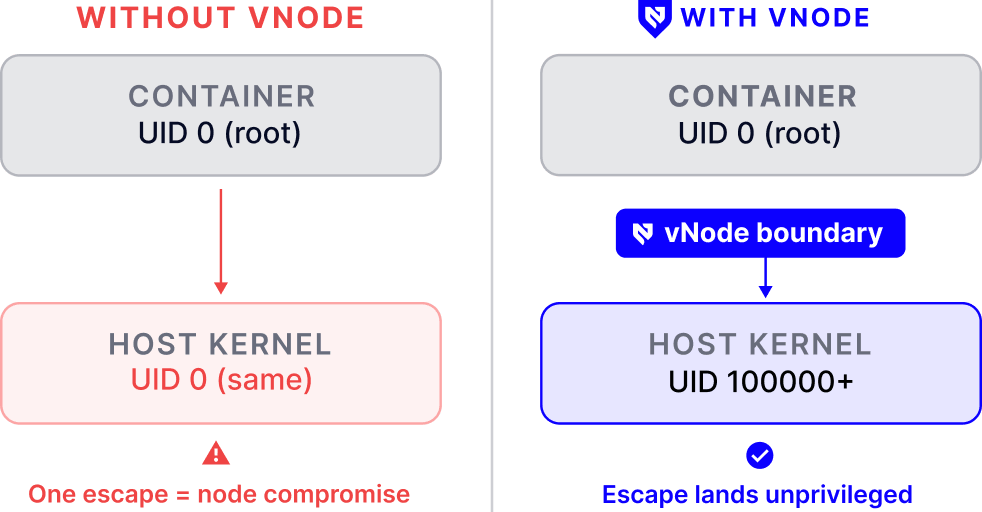
vNode adds a tenant isolation runtime using Linux user namespaces and seccomp filters for workloads that need a stronger runtime boundary.

  • Designed to prevent container breakout
  • No hypervisor performance tax
  • Hardened to the kernel
Network Isolation

Hardware-Enforced Network Boundaries

The Netris integration can place each tenant network environment on a separate hardware-backed L2 boundary.

  • VLANs and VRFs per tenant
  • Network automation via Netris
  • Hardware-enforced network boundaries
Compliance

Air-Gapped and FIPS Deployments

vCluster Platform supports air-gapped deployments and FIPS features on supported plans for regulated deployment patterns.

  • Air-gapped deployment support
  • FIPS features on supported plans
  • Sovereign and regulated environments
Why vCluster

This isn’t a side project. Behind every vCluster deployment is 5+ years of deep K8s engineering, security hardening, and battle-tested infrastructure work at massive scale.

100K+
GPUs Powered
50+
GPU Clouds & F500s
<45
Days to Launch
30K
GitHub Stars

Get Started in 3 Steps

1
Schedule a Demo

Talk to our team about your stack

2
Deploy vCluster

Deploy vCluster on your infra in minutes

3
Onboard Your Tenants

Go live with a hyperscaler-grade tenant experience in days

FAQs

What makes vCluster's GPU cluster isolation stronger than Kubernetes namespaces?

Namespace-only designs share the Kubernetes control plane and node-level components. vCluster gives each tenant a separate virtualized control plane, while Private Nodes assign dedicated worker capacity to each production tenant cluster.

How does vCluster Platform handle GPU workload isolation between tenants?

vCluster handles control plane and worker node isolation, and vNode can add a stronger runtime boundary with Linux user namespaces and seccomp. GPU partitioning (MIG, vGPU, time-slicing, or DRA) stays with the GPU operator and driver stack, and vCluster layers the tenant boundary over it.

Can vCluster support compliance requirements for tenant isolation on GPU infrastructure?

vCluster Platform supports air-gapped deployments and FIPS features on supported plans. Private Nodes and optional Netris network isolation provide deployment controls for regulated environments without claiming compliance on the customer's behalf.

What cluster types can run as isolated tenant environments on vCluster Platform?

vCluster can power managed Kubernetes, Slurm, Ray, inference, and other tenant cluster products. Slurm keeps responsibility for Slurm scheduling through the Slinky integration, and partner platforms such as NVIDIA Run:ai keep their own schedulers.

How quickly can an AI cloud provider deploy tenant isolation on GPU infrastructure with vCluster?

vCluster provides turnkey tenant management and APIs for a custom experience. Templates, capacity policy, and centralized fleet operations reduce the platform work required to launch and operate tenant clusters. Boost Run went from decision to production launch in under 45 days.

Does vCluster's isolation model require provisioning separate physical clusters per tenant?

No separate Kubernetes control-plane servers are required for each tenant. The tenant control plane runs as isolated pods, while Private Nodes provide dedicated worker capacity for production workloads.

See GPU Cluster Isolation in Action

Learn how 50+ GPU clouds implement tenant isolation with vCluster.