InfiniBand Kubernetes Performance Meets Tenant Isolation
Run Kubernetes workloads on InfiniBand-connected GPU servers. vMetal supplies machines, and vCluster separates tenant control planes and dedicates workers through bare metal Private Nodes.
High-performance fabrics demand infrastructure that keeps pace without compromising tenant security.
Dedicated GPU workers do not reserve shared fabric bandwidth. Network partitions and congestion policies must match the workload and tenant design.
Namespace boundaries still share cluster-wide resources. RBAC, admission and network controls must limit tenant access to platform internals.
Provisioning a full physical cluster per tenant wrecks the economics of the InfiniBand fabric and GPUs you've already built.
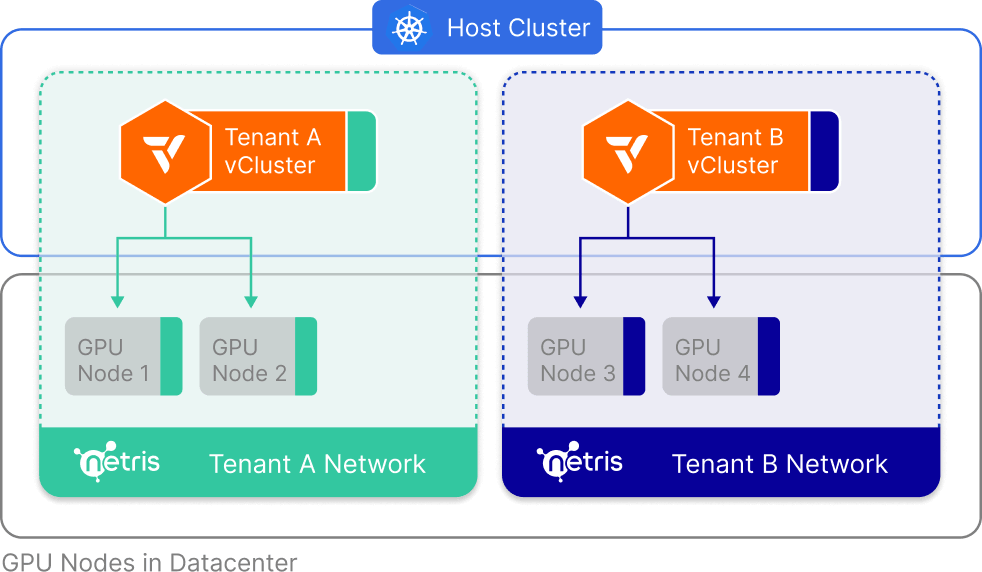
vCluster separates tenant control planes and dedicates InfiniBand-connected workers through bare metal Private Nodes. vMetal manages machines; fabric partitions and bandwidth policies remain distinct from node ownership. vCluster Labs software powers 100K+ GPUs.
The stack from bare metal provisioning through tenant cluster orchestration to workload-level isolation on high-performance fabrics.
Private Nodes dedicate worker capacity to one tenant cluster, with its own CNI and storage configuration. For InfiniBand-connected workloads, select physical servers or VMs according to the required infrastructure boundary.

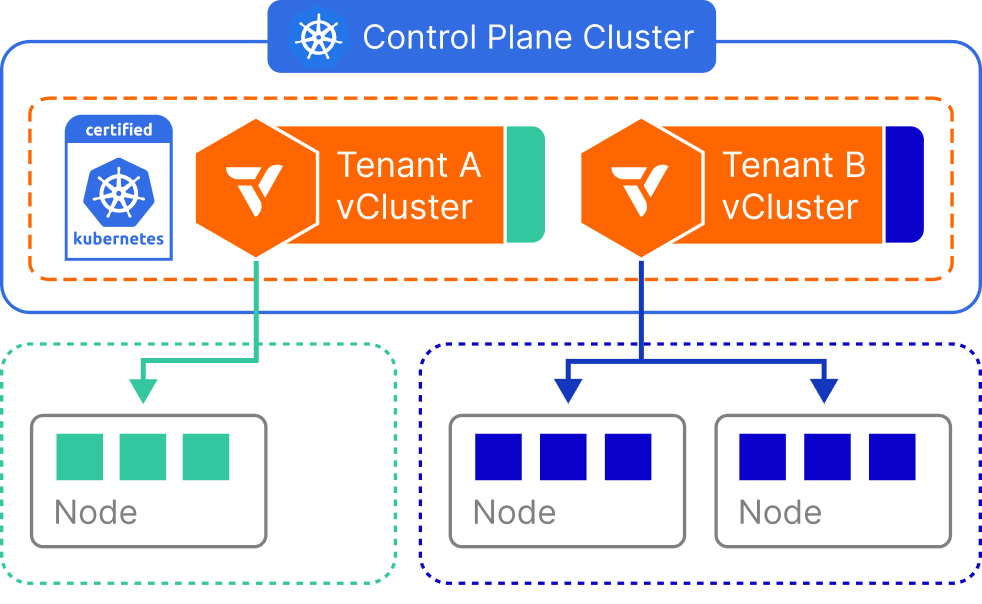
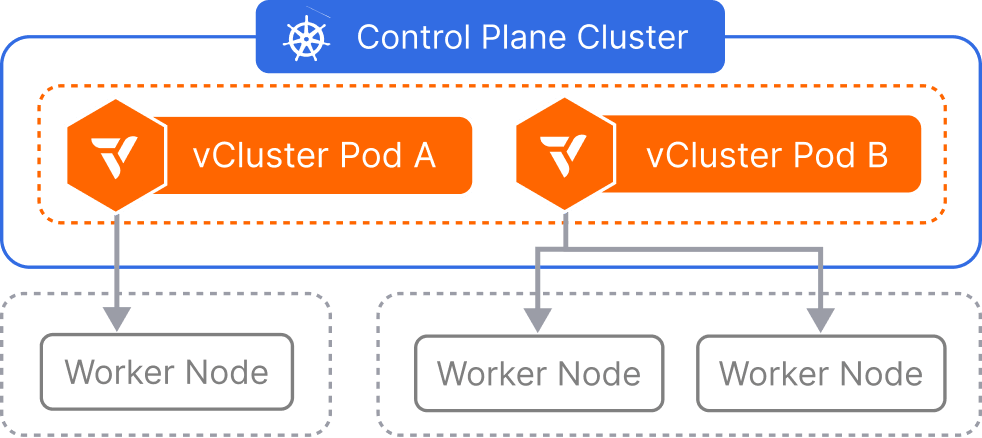
Each tenant has an independent Kubernetes API, data store and RBAC boundary. Lightweight control-plane hosting reduces dedicated server requirements for InfiniBand-connected workloads; Private Nodes keep production workers tenant-specific.

Tenant-owned CNI configuration and supported Netris integrations provide separate network controls for InfiniBand-connected workloads. Ethernet segmentation can use VLANs, VRFs and ACLs; InfiniBand isolation uses fabric partitions rather than Ethernet constructs.

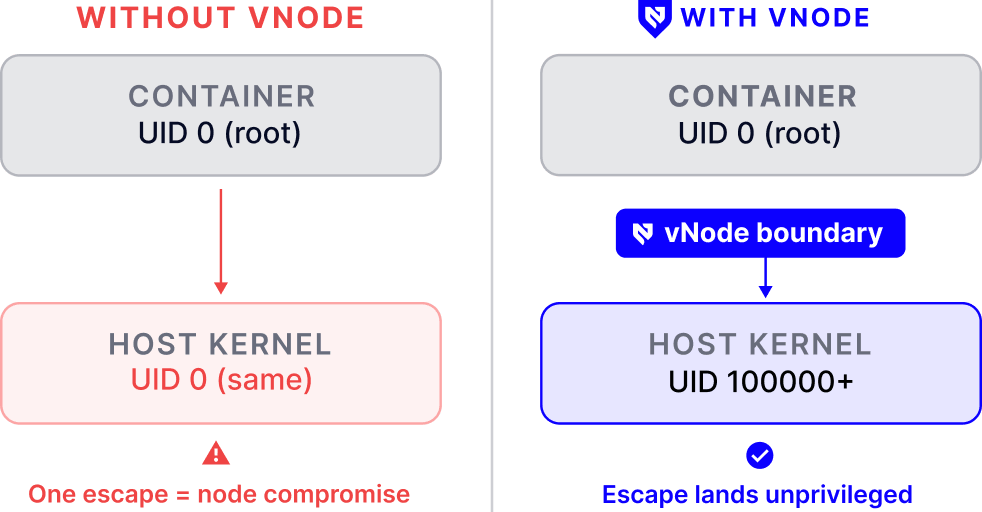
vNode uses Linux user namespaces and seccomp to restrict workload privileges and system calls. It adds runtime hardening for InfiniBand-connected workloads without a guest kernel or hypervisor, complementing dedicated workers rather than allocating GPUs.

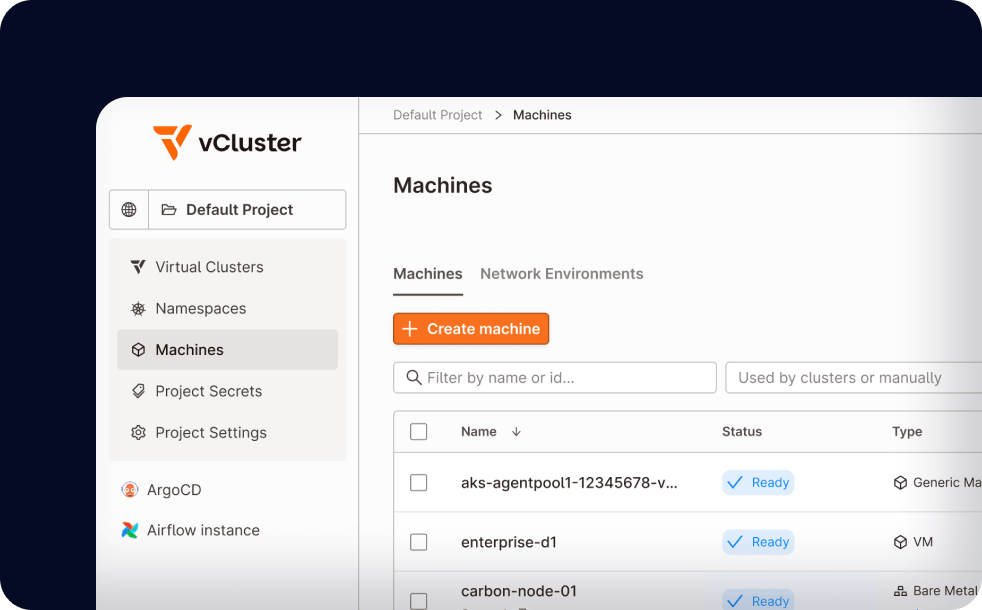
vMetal exposes one Machine API above bare metal and VM provisioning drivers. Registered inventory, images and credentials enable repeatable machine lifecycle workflows for InfiniBand-connected workloads. Network automation uses supported integrations such as Netris.
This isn’t a side project. Behind every vCluster deployment is 5+ years of deep K8s engineering, security hardening, and battle-tested infrastructure work at massive scale.
Talk to our team about your stack
Deploy vCluster on your infra in minutes
Go live with a hyperscaler-grade tenant experience in days
Dedicated Private Nodes remove cross-tenant workload placement from those workers. Bare metal avoids a hypervisor layer, but this is not a throughput or latency guarantee. GPU drivers, workload configuration, network fabrics and storage can still influence performance. vNode adds runtime hardening using the Linux kernel; benchmark the selected stack against the workload and service levels you intend to offer.
vCluster Standalone runs as a Kubernetes binary directly on Linux without requiring another Kubernetes cluster, k3s or kubeadm. It can provide an initial Kubernetes foundation. vMetal is a separate infrastructure orchestration layer that requires vCluster Platform and a connected Kubernetes cluster for its Metal3/Ironic path. Hardware registration, images, credentials and driver setup remain prerequisites for machine provisioning.
Private Nodes are worker nodes joined to one tenant cluster, with that tenant's own CNI and storage configuration. They can be physical machines or supported VMs. Use dedicated bare metal when the service requires exclusive physical servers. vMetal can provision the underlying machines, while platform policies define which capacity a tenant may request and how it is released.
vCluster is a CNCF-certified Kubernetes distribution and exposes standard Kubernetes APIs in tenant environments. This supports familiar clients, Helm charts and cluster-scoped resources such as CRDs. Certification covers Kubernetes conformance rather than an entire AI platform or customer deployment. Validate the selected version, networking, storage, GPU drivers and runtime integrations for the workloads you plan to support.
vCluster Labs software powers 100K+ GPUs and 1M+ CPUs, serving 50+ GPU clouds & Fortune 500s combined. In production, Lintasarta operates 170+ tenant clusters, while Boost Run completed its managed Kubernetes launch in under 45 days from the decision. These named deployments provide scale and launch examples for teams evaluating the platform for their own infrastructure.
Netris supports InfiniBand partition orchestration through its NVIDIA UFM integration, using partition keys. VLANs, VXLANs and VRFs apply to Ethernet segmentation instead. vCluster supplies tenant control-plane and worker boundaries; the supported integration chain must also configure the fabric. Dedicated GPU servers do not by themselves reserve InfiniBand bandwidth, so fabric access and performance policies remain separate operational requirements.
See how GPU cloud providers deploy tenant isolation on bare metal without sacrificing performance.