platform-eng
Kubernetes Hardware Isolation for AI Workloads
Use Private Nodes backed by dedicated physical servers for Kubernetes hardware isolation. Each tenant also receives its own virtualized control plane and RBAC boundary.
Use Private Nodes backed by dedicated physical servers for Kubernetes hardware isolation. Each tenant also receives its own virtualized control plane and RBAC boundary.
Namespace boundaries do not dedicate physical worker capacity to a tenant cluster.
Namespace-only designs share the API server and can also share worker nodes between tenants.
Building and operating a separate Kubernetes management stack for every tenant increases infrastructure work.
Shared worker nodes expose workloads to cross-tenant contention for CPU, GPU, memory, network, and storage resources.
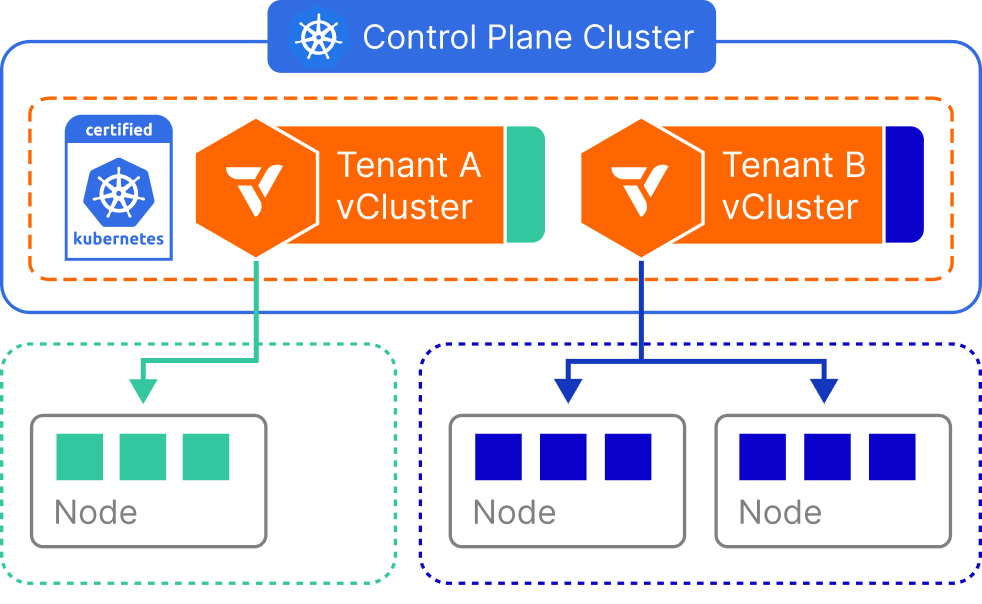
vCluster Platform uses Private Nodes as the production default. When backed by dedicated physical servers, Private Nodes provide Kubernetes hardware isolation while virtualized control planes avoid separate control-plane servers per tenant.
Kubernetes hardware isolation combines dedicated physical Private Nodes with a separate tenant control plane and optional runtime and network controls.
Assign dedicated physical worker nodes, networking, and storage to one production tenant cluster at a time.
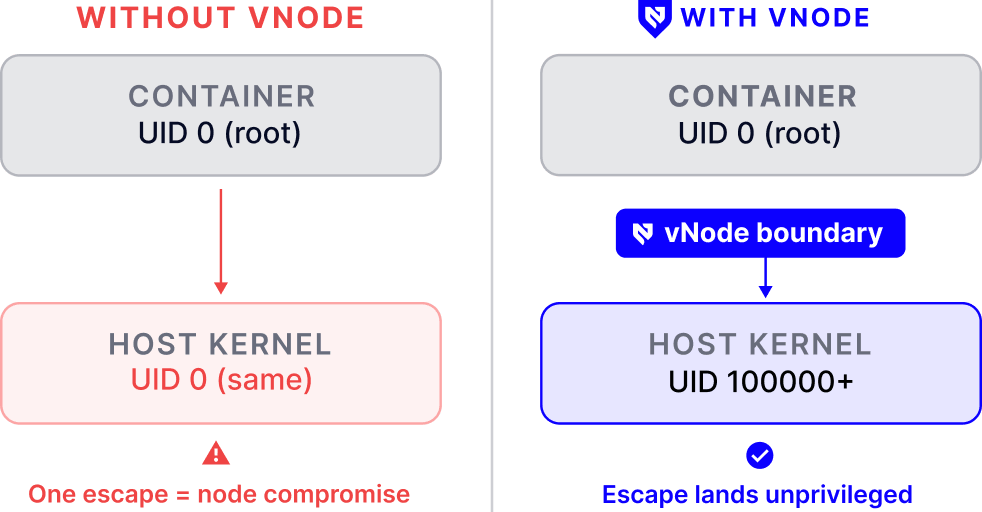
vNode uses Linux user namespaces and seccomp filters to strengthen the runtime boundary for workloads that need additional isolation.
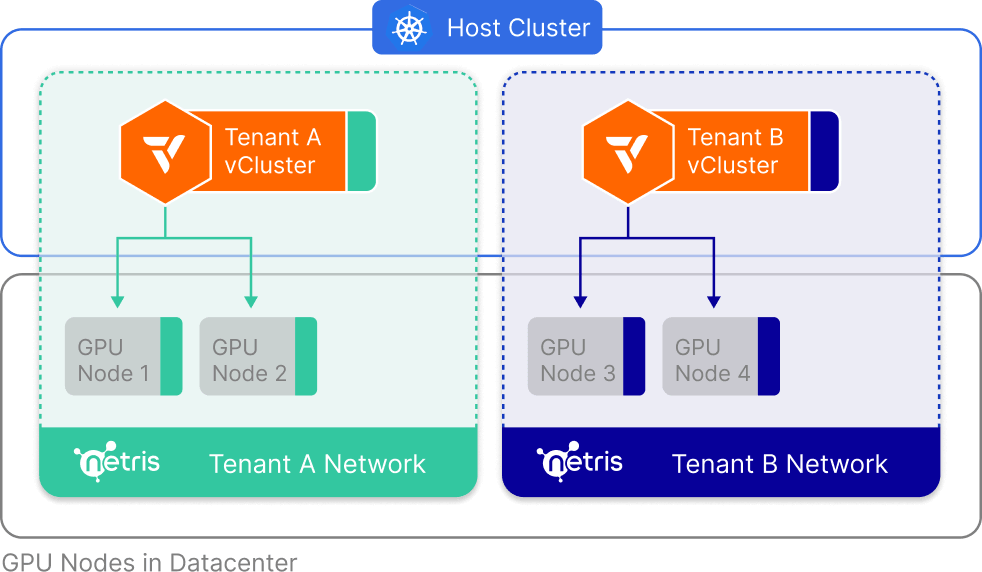
Metal3 and Netris can place separate tenant network environments on hardware-backed L2 boundaries when configured.
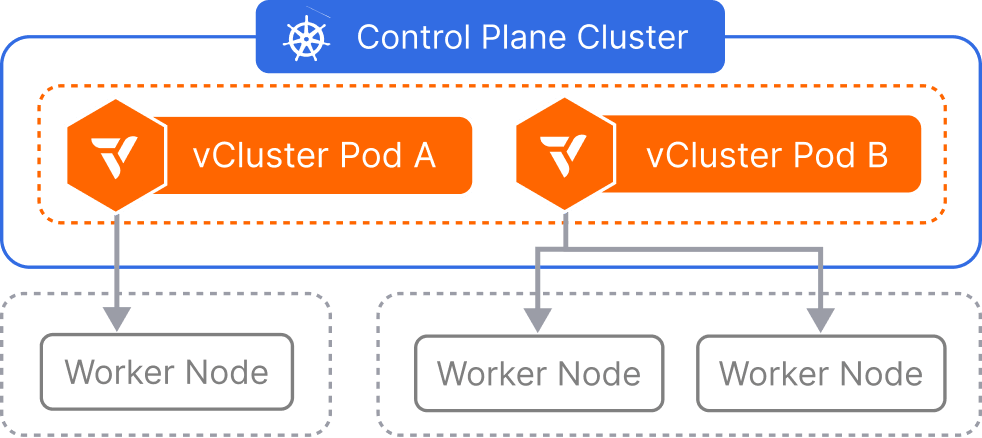
Every tenant cluster receives its own virtualized API server and RBAC boundary on the control plane cluster.
vCluster Platform supports air-gapped deployments and FIPS features on supported plans for controlled infrastructure environments.
This isn’t a side project. Behind every vCluster deployment is 5+ years of deep K8s engineering, security hardening, and battle-tested infrastructure work at massive scale.
Talk to our team about your stack
Deploy vCluster on your infra in minutes
Go live with a hyperscaler-grade tenant experience in days
Kubernetes hardware isolation assigns physical worker nodes to one tenant cluster at a time. The tenant's workloads do not share CPU, GPU, memory, networking, or storage components on those dedicated servers with another tenant cluster.
Private Nodes are the production default. When those nodes are dedicated physical servers, they provide the hardware boundary. vCluster also gives each tenant its own virtualized control plane and RBAC boundary.
Yes. The tenant control plane runs as isolated pods on a control plane cluster, so every tenant does not need separate physical control-plane servers. Production worker capacity remains dedicated through Private Nodes.
Dedicated Private Nodes remove cross-tenant workload placement from those servers. Actual GPU throughput still depends on the hardware, driver stack, network, storage, and workload configuration.
vCluster Platform supports air-gapped deployments and FIPS features on supported plans. With Metal3 and Netris configured, separate network environments can provide hardware-backed L2 isolation.
vCluster powers 100K GPUs across 50+ GPU Clouds & Fortune 500s and is validated in the NVIDIA DGX reference architecture.
See how Private Nodes provide Kubernetes hardware isolation for production tenant clusters.
