Namespace Per Customer Kubernetes With Tenant Isolation
Move beyond namespace per customer Kubernetes for production tenants. vCluster gives each customer a separate Kubernetes control plane and uses Private Nodes for dedicated worker capacity.
Namespace per customer Kubernetes shares control-plane and often worker-node components between customers.
Namespaces share the Kubernetes API server and cluster-level components between customers.
A separate management stack for every customer increases infrastructure and operational work.
Building custom tenant isolation requires ongoing work across access, capacity, networking, observability, and lifecycle operations.
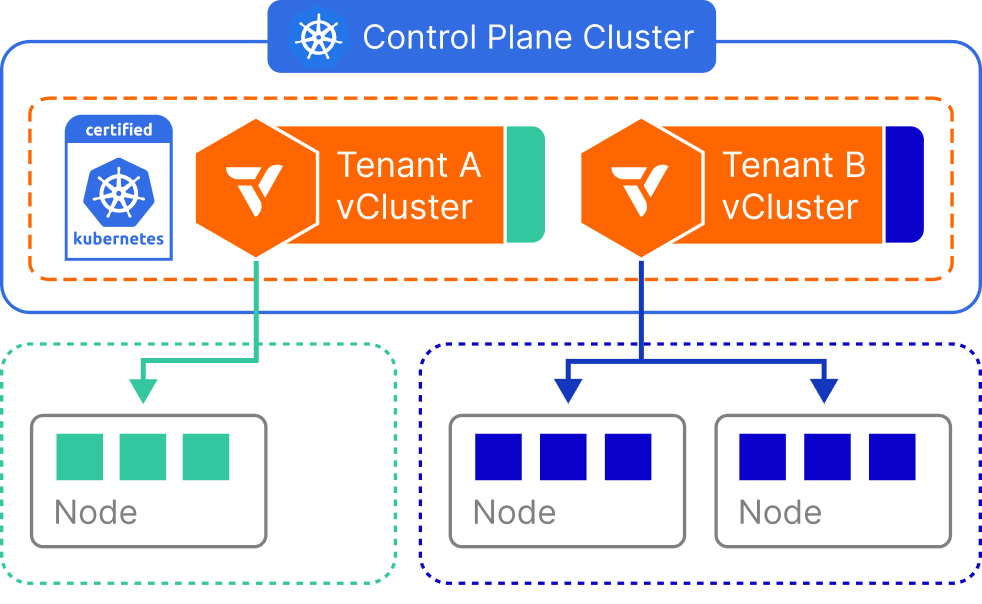
vCluster Platform gives each customer a separate tenant cluster with its own virtualized control plane. Private Nodes provide dedicated production worker capacity while operators retain central policy and fleet control.
Move beyond namespace per customer Kubernetes with separate tenant control planes, Private Nodes, and centralized operations.
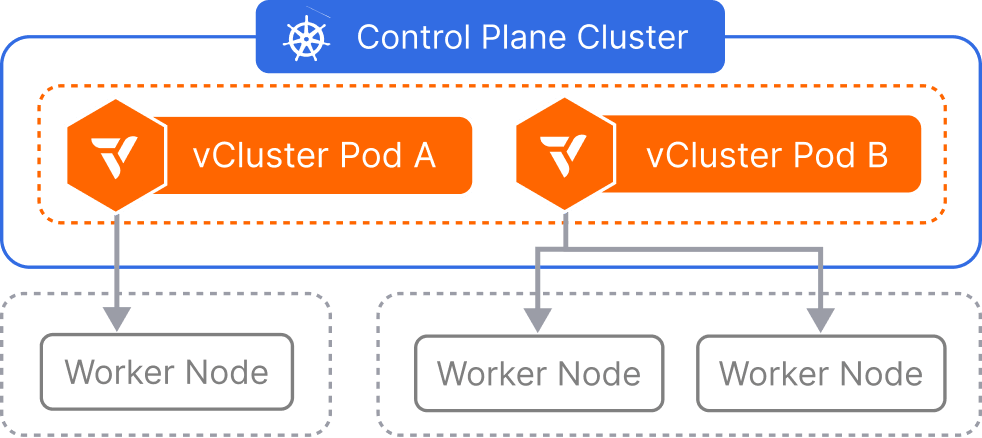
Private Nodes dedicate worker capacity, networking, and storage to one production customer cluster at a time.

Each customer receives a separate virtualized API server and RBAC boundary on the control plane cluster.

Tenant clusters use a certified Kubernetes distribution and standard APIs for existing tools, CRDs, and operators.
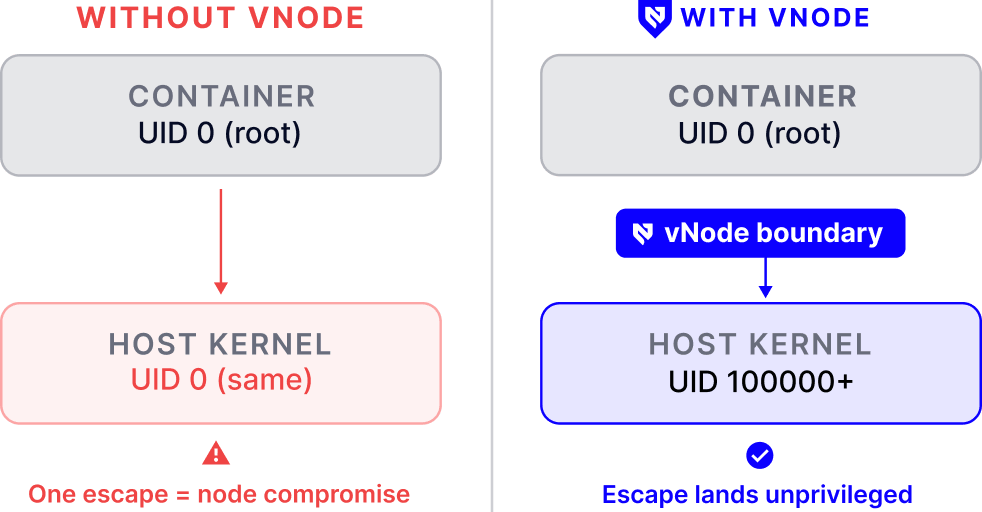
vNode uses Linux user namespaces and seccomp filters to strengthen the runtime boundary for workloads that need additional isolation.

vCluster Platform supports air-gapped deployments and FIPS features on supported plans for controlled environments.

This isn’t a side project. Behind every vCluster deployment is 5+ years of deep K8s engineering, security hardening, and battle-tested infrastructure work at massive scale.
Talk to our team about your stack
Deploy vCluster on your infra in minutes
Go live with a hyperscaler-grade tenant experience in days
Namespace per customer Kubernetes shares one API server and node-level components across customers. That model fits trusted internal teams, but external or untrusted production tenants need a stronger control-plane and worker-node boundary.
vCluster gives each customer a separate virtualized API server and RBAC boundary. Private Nodes are the production default and dedicate worker capacity, networking, and storage to one tenant cluster at a time.
Yes. Customers can receive cluster-admin inside their own tenant cluster, including control of CRDs and RBAC, without access to the provider's control plane cluster or another tenant environment.
vCluster Platform supports air-gapped deployments and FIPS features on supported plans. Compliance still depends on the customer's complete deployment, configuration, and operating controls.
Virtualized control planes are lightweight and can be created quickly. Private Node readiness depends on whether worker capacity is available or must be provisioned.
vCluster powers 100K GPUs across 50+ GPU Clouds & Fortune 500s and provides centralized operations for tenant cluster fleets.
See how vCluster Platform supports namespace per customer kubernetes with tenant isolation.