ai-cloud

Network Isolation GPU Cluster for AI Clouds

On a GPU cluster, network isolation has to keep one tenant's traffic off another's path, ideally in the switch fabric as well as in software. Private Nodes give each tenant its own workers and CNI, and Netris adds per-tenant VLANs, VRFs and ACLs.

Trusted by the fastest-growing AI cloud providers
Problem

Network Isolation on GPU Clusters Is Hard

GPU clusters serving several tenants need network boundaries that match the trust level of each tenant.

Namespace Isolation Is Too Weak

Namespace-only designs depend on shared cluster and network components that are unsuitable for untrusted tenants.

Separate Physical Clusters Are Too Expensive

A separate management stack for every tenant adds infrastructure and operational work.

DIY Network Segmentation Breaks Down at Scale

Manual network configuration becomes harder to apply consistently as tenant environments change.

Solution

Hardware-Level Network Isolation Per Tenant Cluster

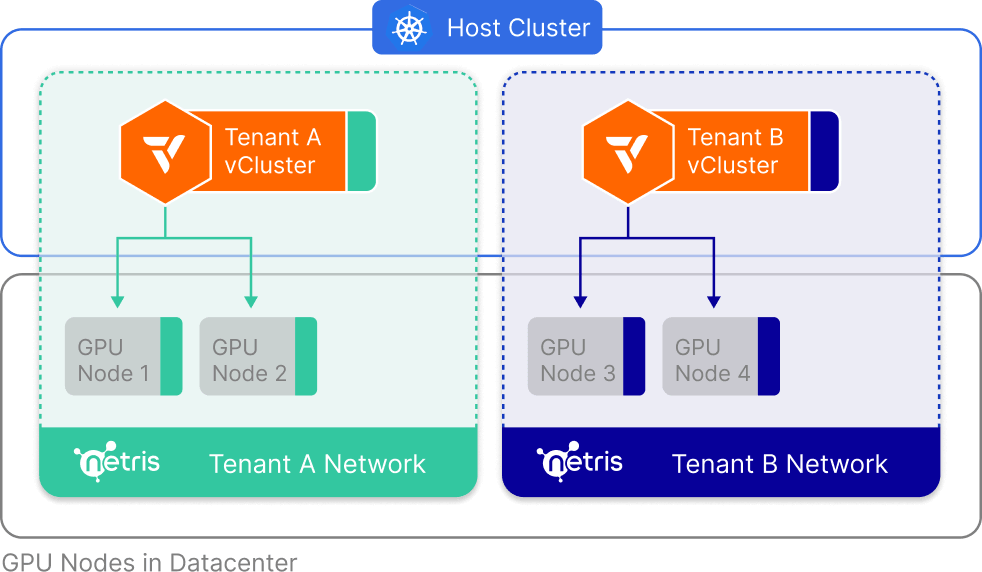
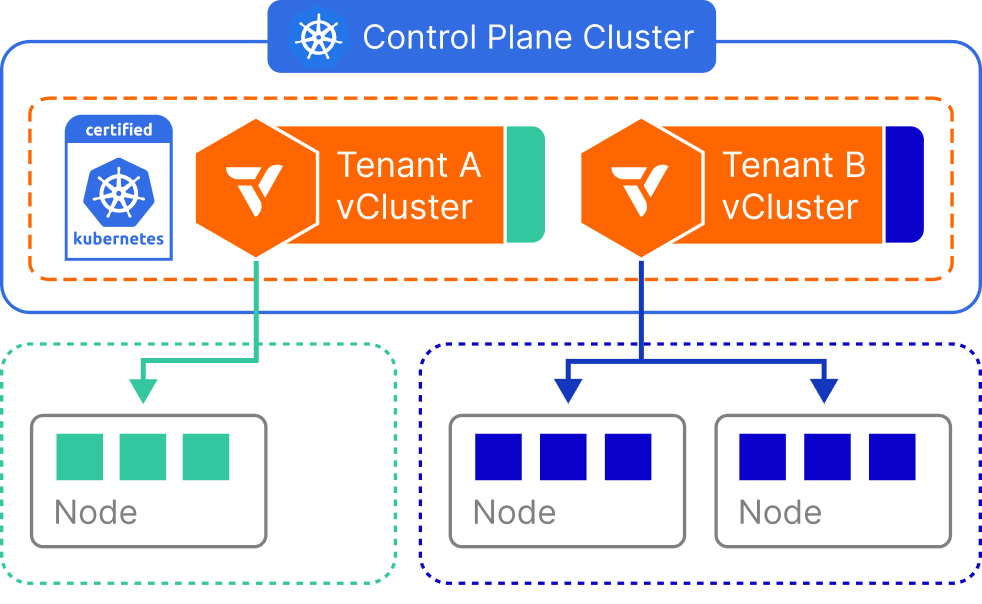
Private Nodes keep each production tenant's workloads on its own worker nodes, and Netris moves the network boundary into the physical fabric with per-tenant VLANs, VRFs, and ACLs. A separate virtualized control plane covers the API server and RBAC layer.
Isolation Features Built for GPU Cluster Scale

Combine isolated tenant control planes, Private Nodes, and optional Netris hardware network isolation for GPU infrastructure.

Network Isolation

Per-Tenant VLANs, VRFs, and ACLs

The Netris integration attaches each tenant network environment to its own hardware-backed L2 boundary.

  • Hardware-enforced per-tenant network boundaries
  • VLANs, VXLANs, VRFs, and ACLs automated
  • Netris network automation
Hardware Isolation

Private Nodes With Per-Tenant CNI

Private Nodes dedicate physical or virtual worker capacity, networking, and storage to one tenant cluster at a time.

  • Dedicated GPU nodes per tenant
  • Per-tenant CNI and storage stack
  • No shared hardware between tenants
Workload Security

Kernel-Native Workload Isolation

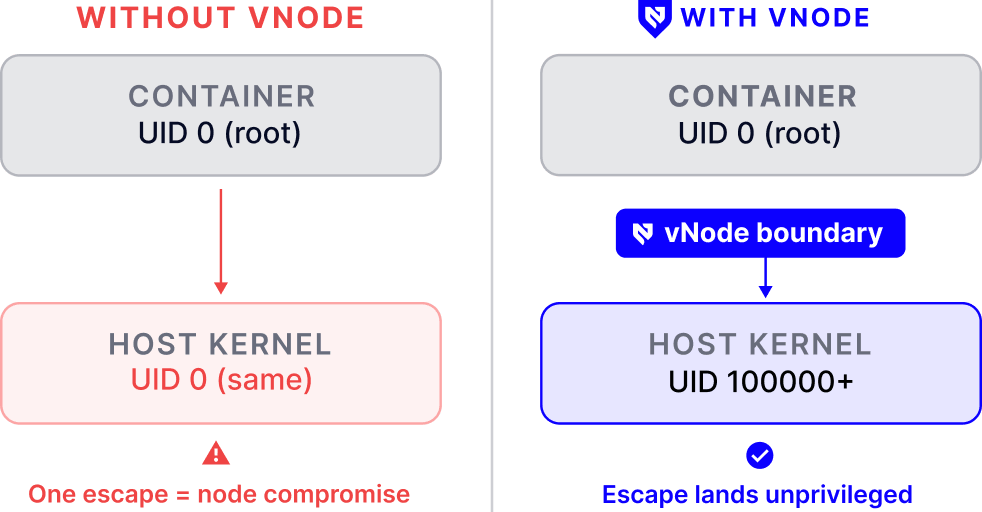
vNode uses Linux user namespaces and seccomp filters to strengthen the runtime boundary for tenant workloads and is designed to help prevent container breakout.

  • User namespaces and seccomp
  • No VM layer on bare metal performance
  • Stronger runtime boundary
Tenant Clusters

Isolated Control Planes Per GPU Tenant

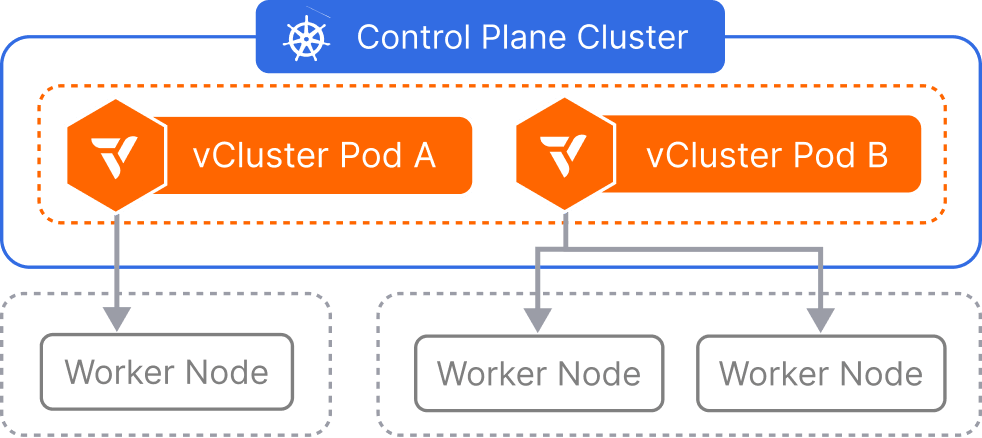
Every tenant cluster gets its own virtualized API server and RBAC boundary on the control plane cluster.

  • Own API server and etcd per tenant
  • Tenant clusters in minutes, not hours
  • Own RBAC per tenant cluster
Compliance

Air-Gapped and FIPS-Ready Deployments

vCluster Platform supports air-gapped deployments and FIPS features on supported plans for regulated deployment patterns.

  • Air-gapped data center deployment supported
  • FIPS features on supported plans
  • Regulated deployment patterns

Why vCluster

This isn’t a side project. Behind every vCluster deployment is 5+ years of deep K8s engineering, security hardening, and battle-tested infrastructure work at massive scale.

100K+
GPUs Powered
50+
GPU Clouds & F500s
<45
Days to Launch
30K
GitHub Stars

Get Started in 3 Steps

1
Schedule a Demo

Talk to our team about your stack

2
Deploy vCluster

Deploy vCluster on your infra in minutes

3
Onboard Your Tenants

Go live with a hyperscaler-grade tenant experience in days

FAQs

How does vCluster enforce network isolation between GPU cluster tenants?

Private Nodes give each production tenant dedicated worker nodes and tenant-scoped networking. With vMetal and the Netris integration configured, each tenant network environment can get its own hardware-backed L2 boundary, enforced with VLANs, VRFs, and ACLs in the switch fabric.

Is this stronger than Kubernetes namespace-based network isolation?

In our analysis, namespace and NetworkPolicy controls operate inside shared cluster and network infrastructure. Private Nodes separate worker capacity, and Netris can move the network boundary into the physical fabric for untrusted tenants.

Can I run a network isolation GPU cluster without provisioning separate physical clusters?

Yes. The tenant control plane runs as isolated pods on the control plane cluster, so it does not require separate control-plane servers. Private Nodes still provide dedicated production worker capacity.

Does hardware-level network isolation affect GPU performance?

Private Nodes run tenant workloads directly on their assigned worker nodes. vNode can add a stronger runtime boundary without adding a VM layer, while the GPU driver and device plugin remain responsible for presenting GPU resources.

Does vCluster support compliance requirements for isolated GPU clusters?

vCluster Platform supports air-gapped deployments and FIPS features on supported plans. Netris network integration provides hardware-backed L2 isolation when configured for separate tenant network environments.

How quickly can I deploy a network-isolated GPU cluster environment?

Tenant control planes come up in minutes, not hours. Bare metal provisioning time depends on the infrastructure driver, server state, OS image, and network configuration.

Ship Hard Network Isolation at GPU Scale

See how vCluster and Netris deliver per-tenant VLANs alongside Private Nodes.