Built for Secure Tenant Kubernetes at Scale
vCluster combines isolated tenant control planes, Private Nodes, optional runtime isolation, and standard Kubernetes APIs.
Hardware Isolation
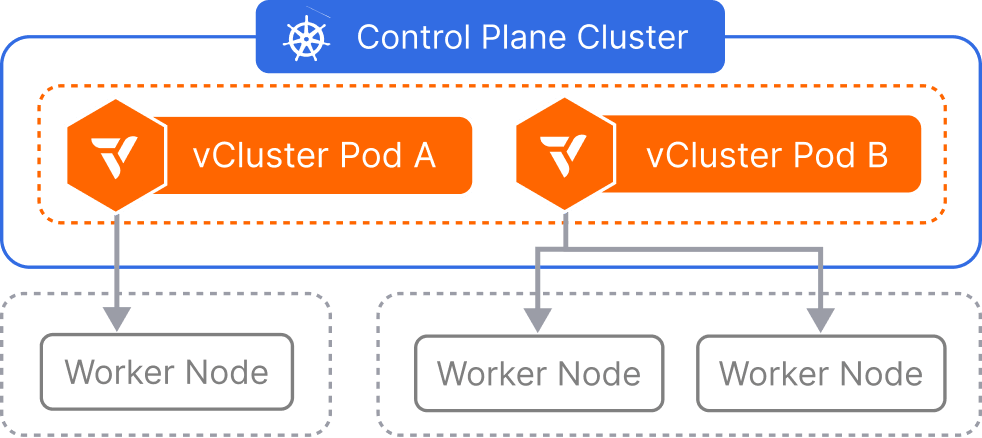
Private Nodes Per Tenant Cluster
Private Nodes dedicate worker capacity, networking, and storage to each production tenant cluster.
Per-tenant CNI and storage
No shared hardware between tenants
Hardware-level isolation by default
Control Plane
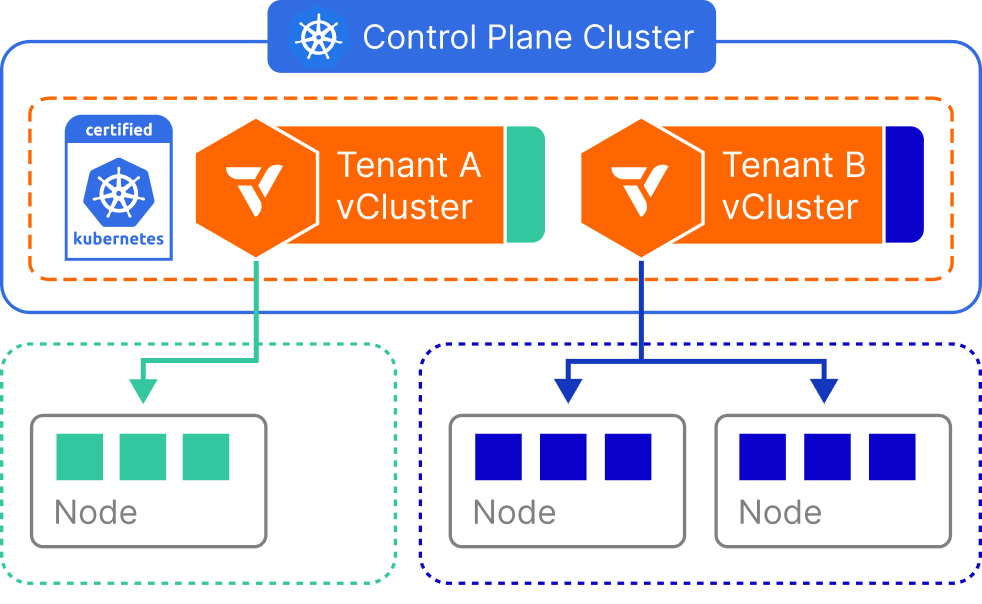
Private Control Plane Per Tenant
Every tenant gets its own virtualized Kubernetes control plane, API server, and RBAC boundary.
Own API server and etcd per tenant
Lightweight control plane
No shared control plane risk
Workload Security
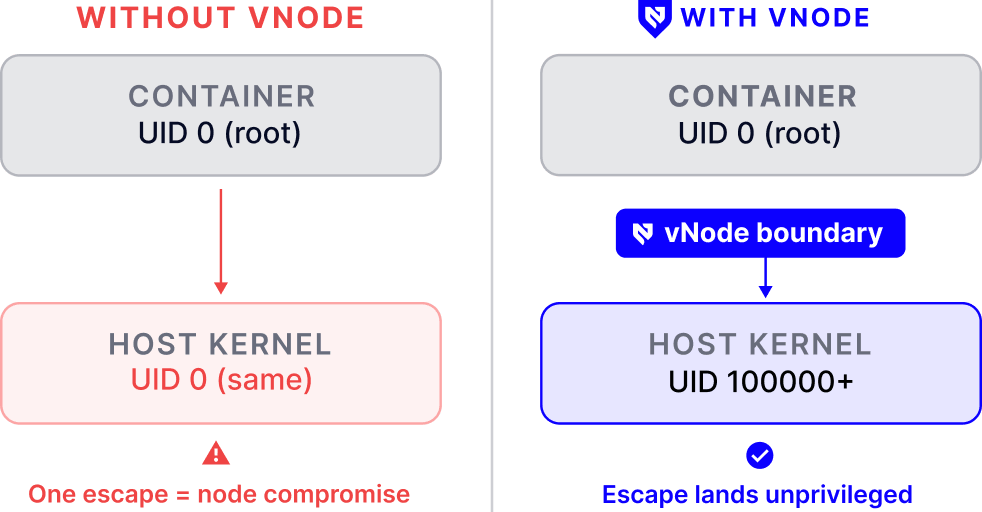
Kernel-Level Workload Isolation
vNode uses Linux user namespaces and seccomp filters to provide a stronger runtime boundary for tenant workloads.
Network Security
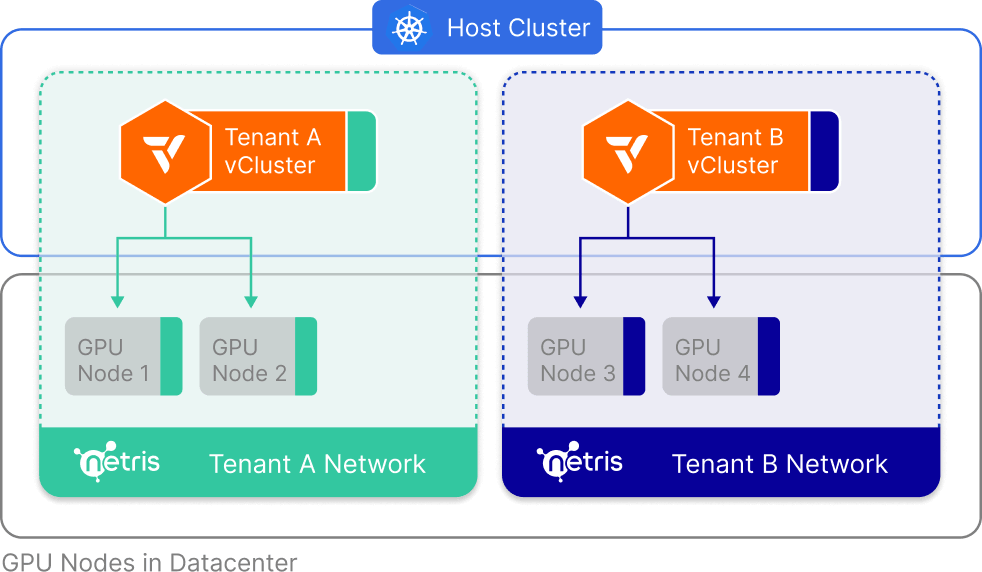
Hardware Enforced Network Isolation
Netris integration can provide hardware-backed L2 isolation through a separate network environment for each tenant.
Standards Compliance
CNCF Certified Kubernetes Per Tenant
Tenant clusters use a certified Kubernetes distribution and standard APIs for existing workloads, tools, CRDs, and operators.